Search and alerts
Search every published leak yourself. Alerts on your keywords. Nothing logged.
From
3 000 €
excl. VAT a year, per organisation
Dark web monitoring for you and your suppliers
What ransomware groups have published about you and your suppliers. Your supplier won’t tell you. The leak will.
If we miss a significant leak about you, next year is free.
They take everything. Military secrets, trade secrets, HR files, even how to reach a site or a person.
It gets used later. By the next attacker, a competitor, a state. Some laws say you have to know.
We read it first, and hand you what concerns you.
We take every file they publish, down to the last zip.
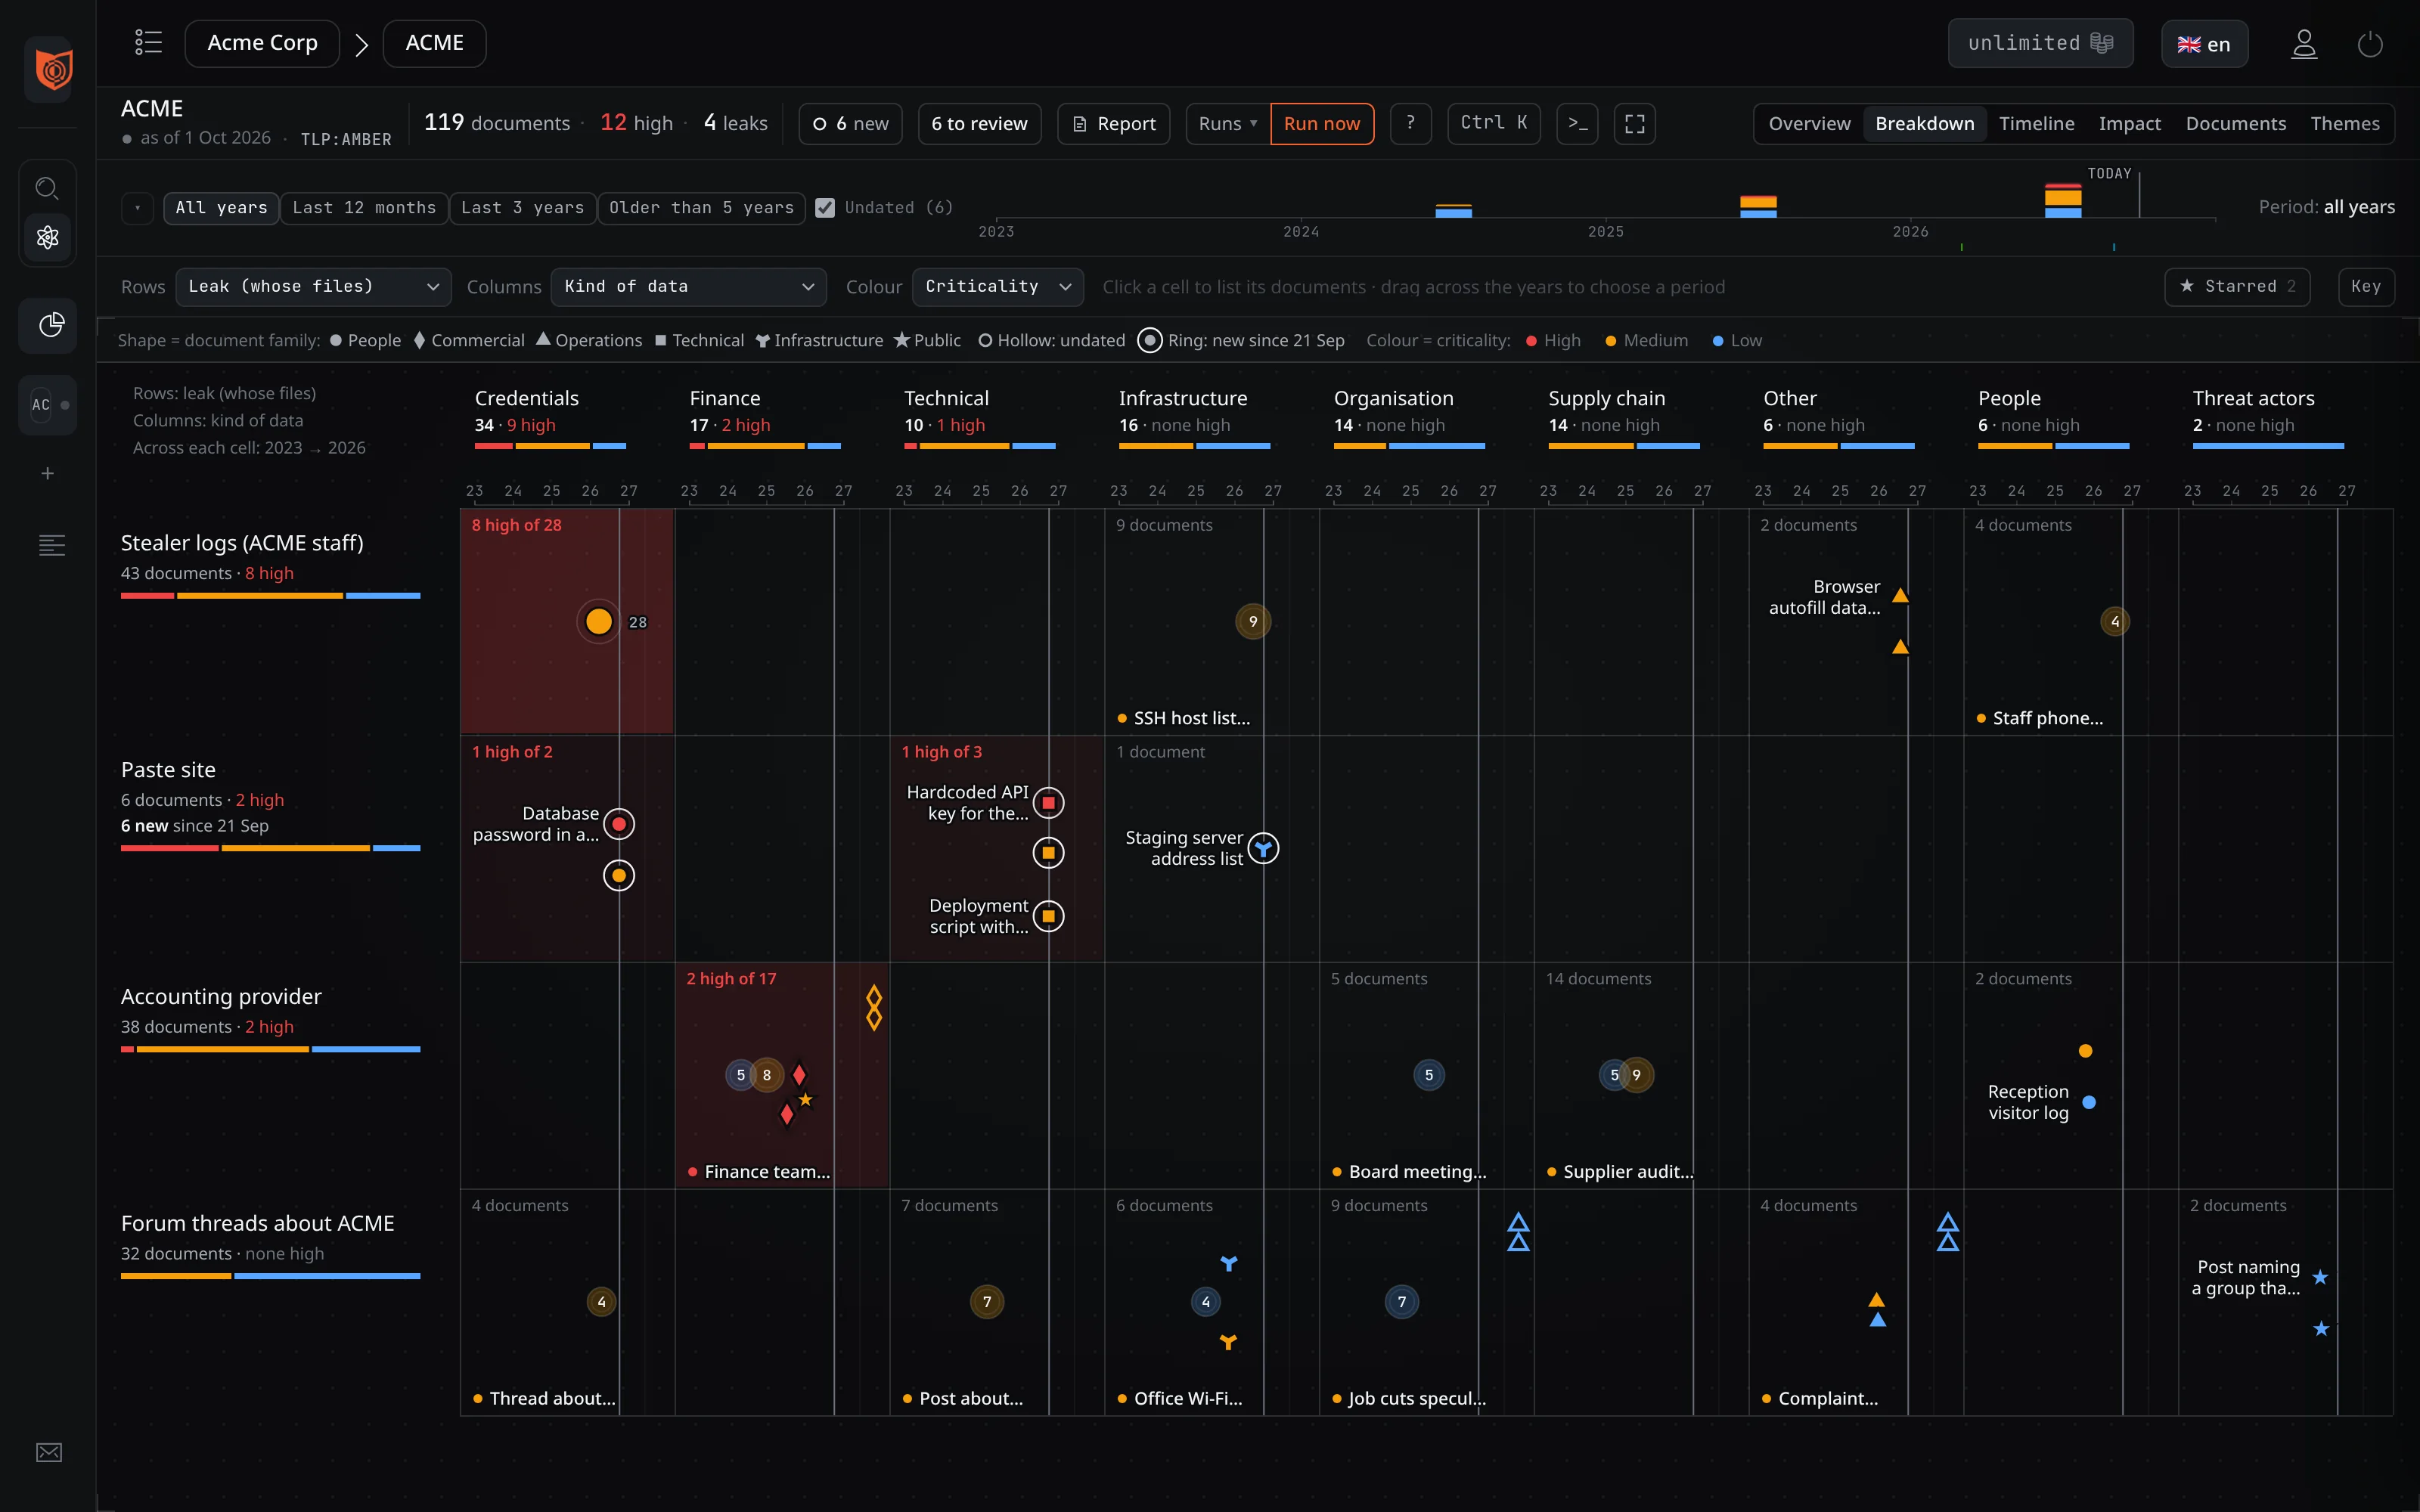
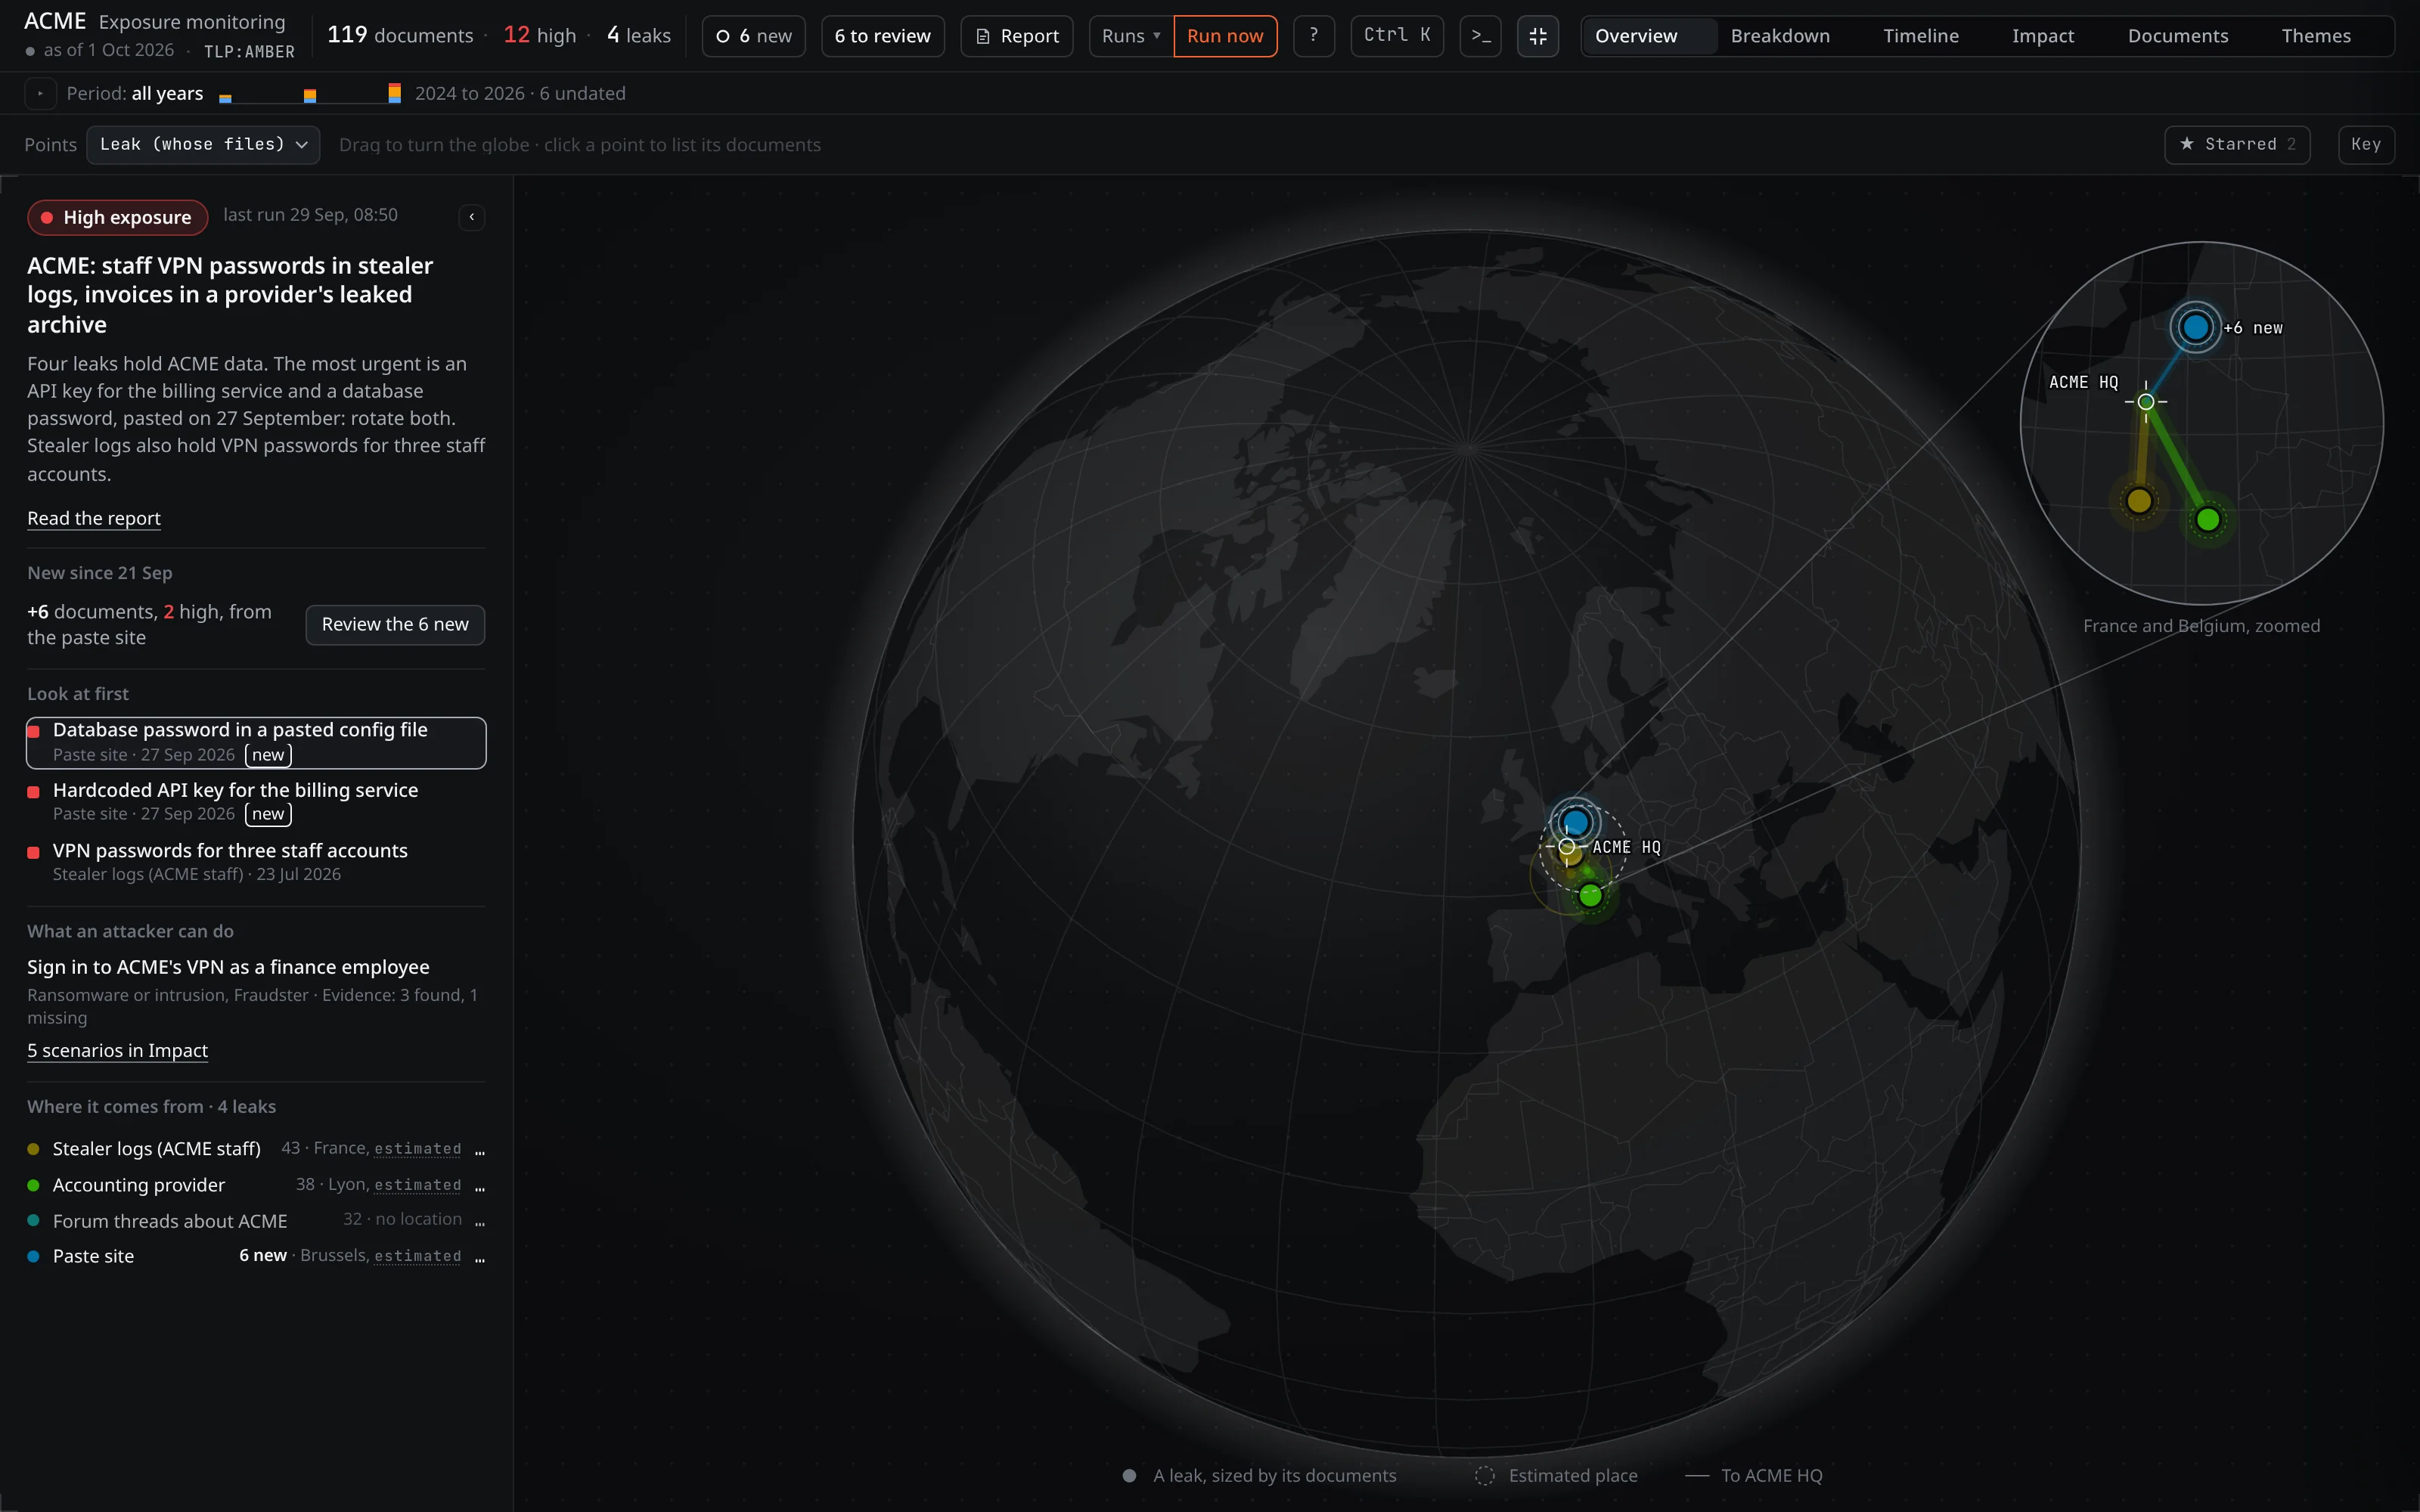
Monitoring, Breakdown · demo data
We read every file. Any format, any language, a binary, a zip inside a zip. What it is. Who it is about.
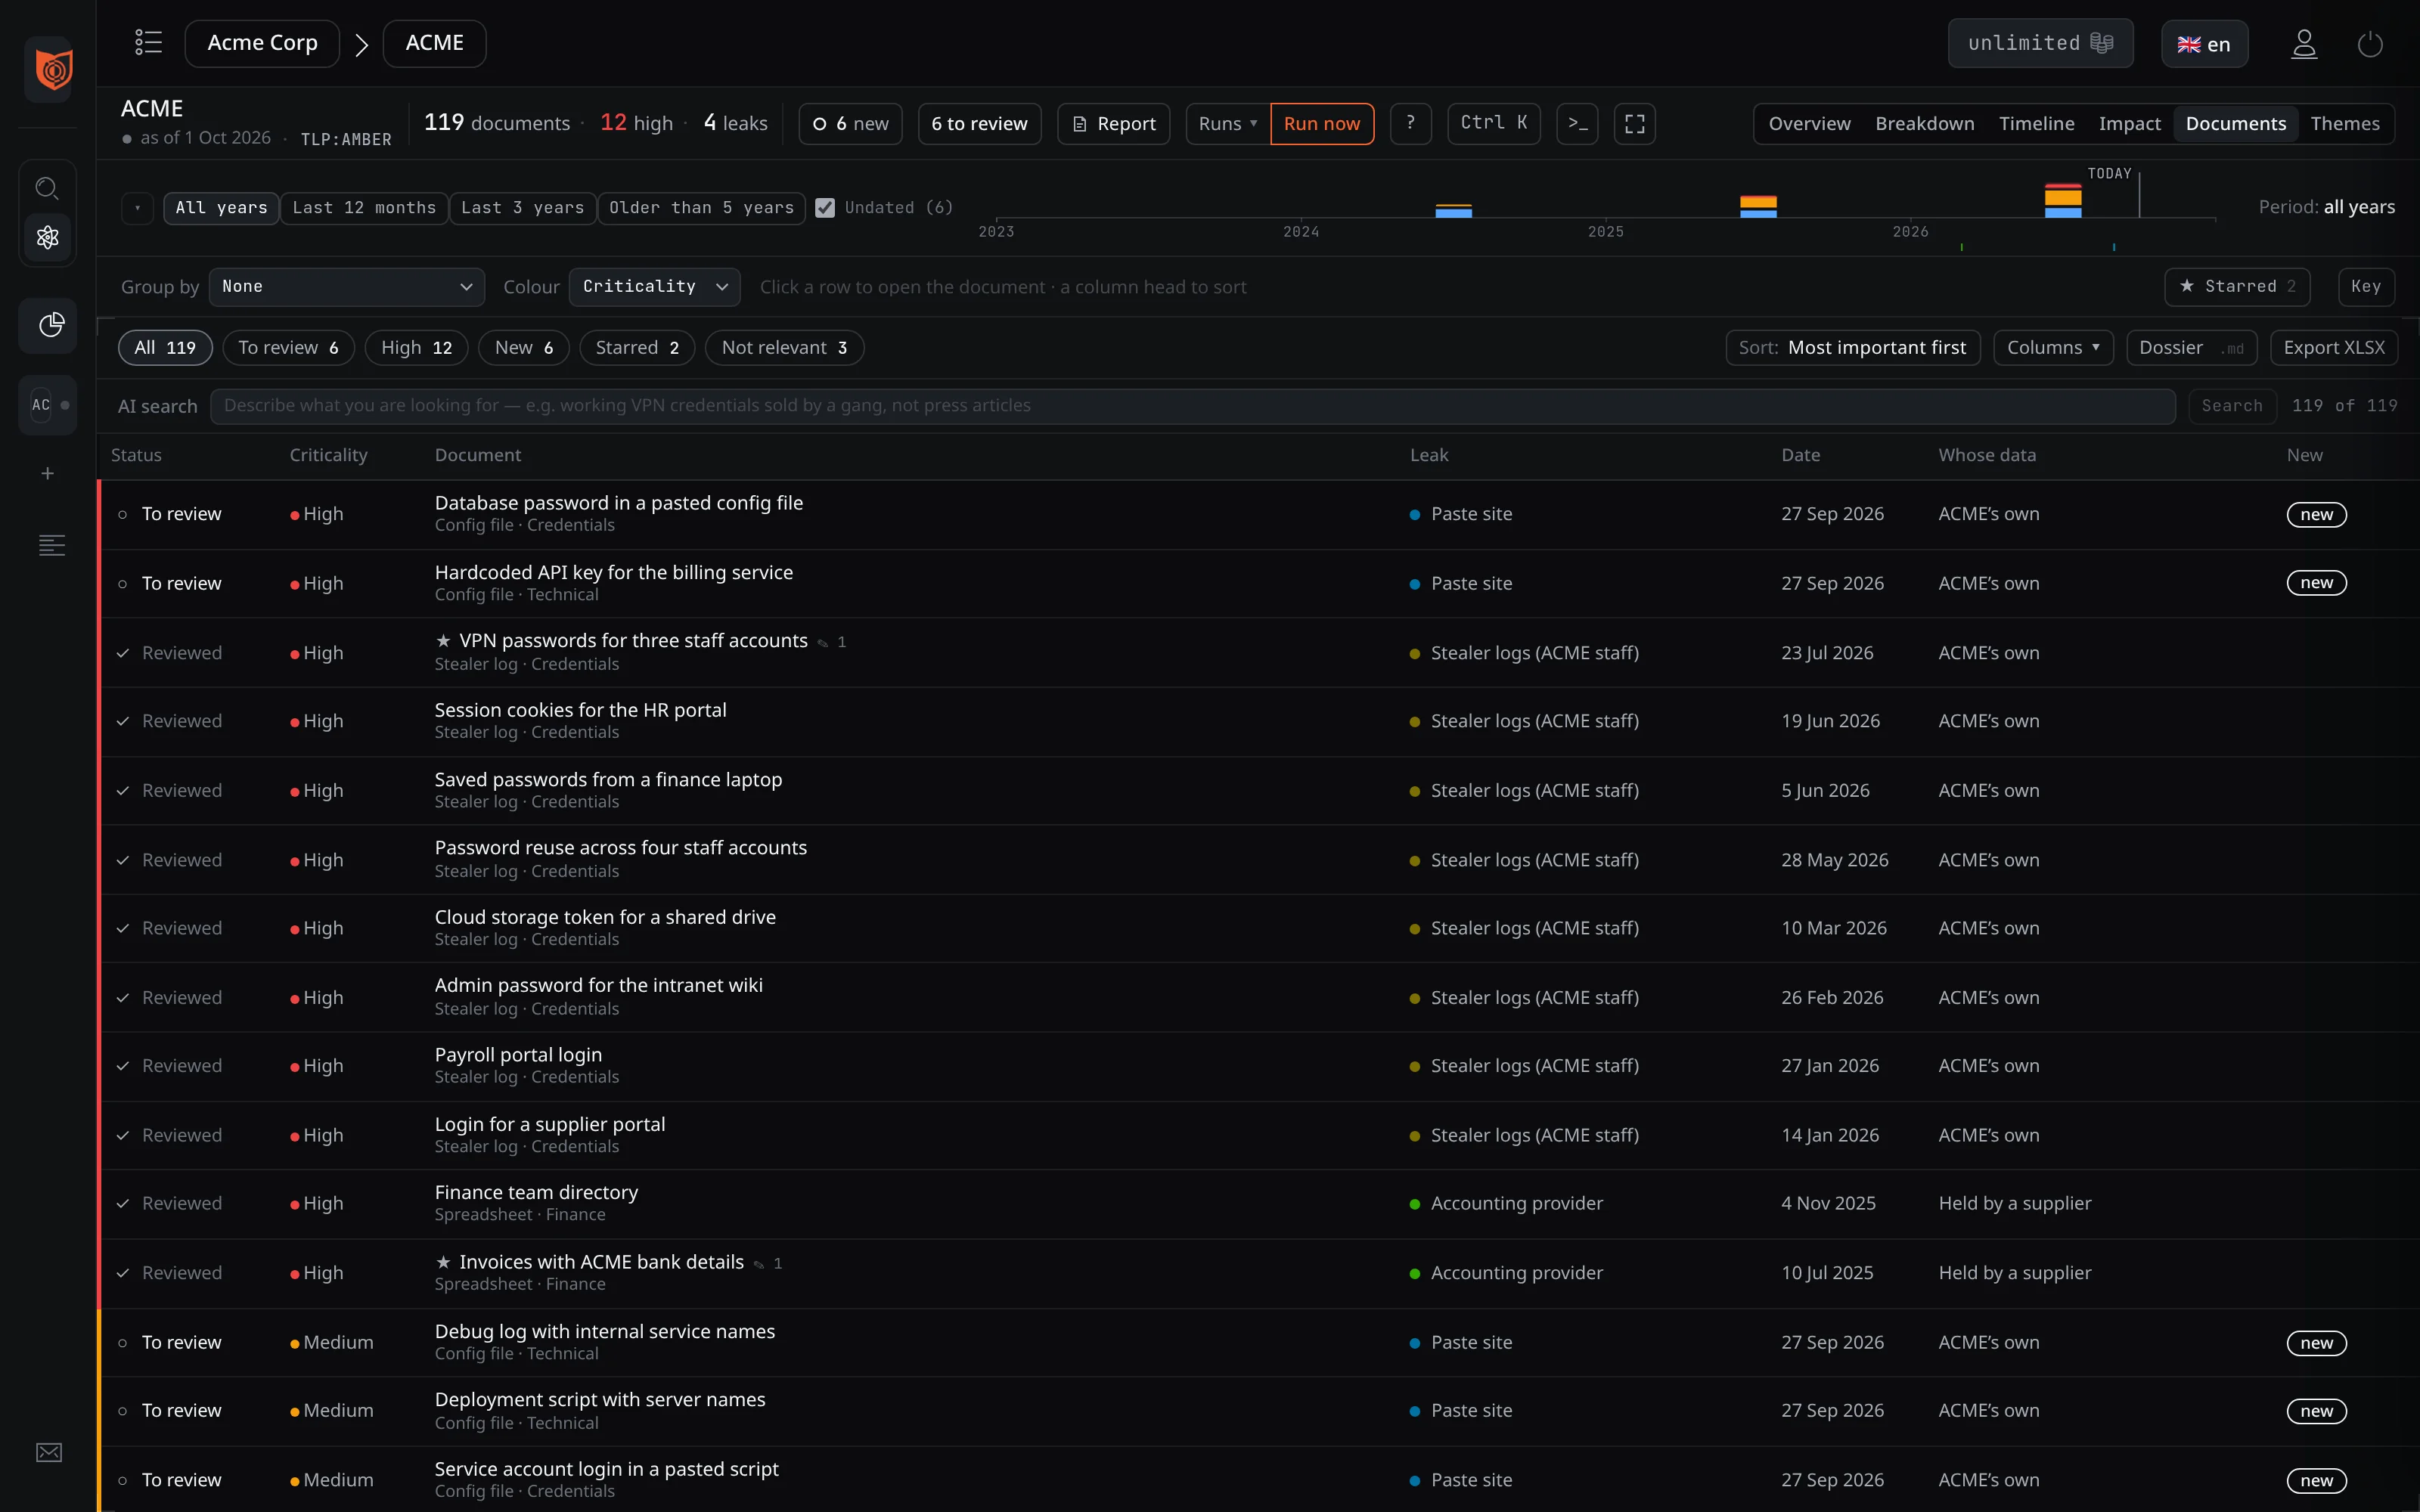
Monitoring, Documents · demo data
One page per document that concerns you: the line, what it means, who on your side should act.
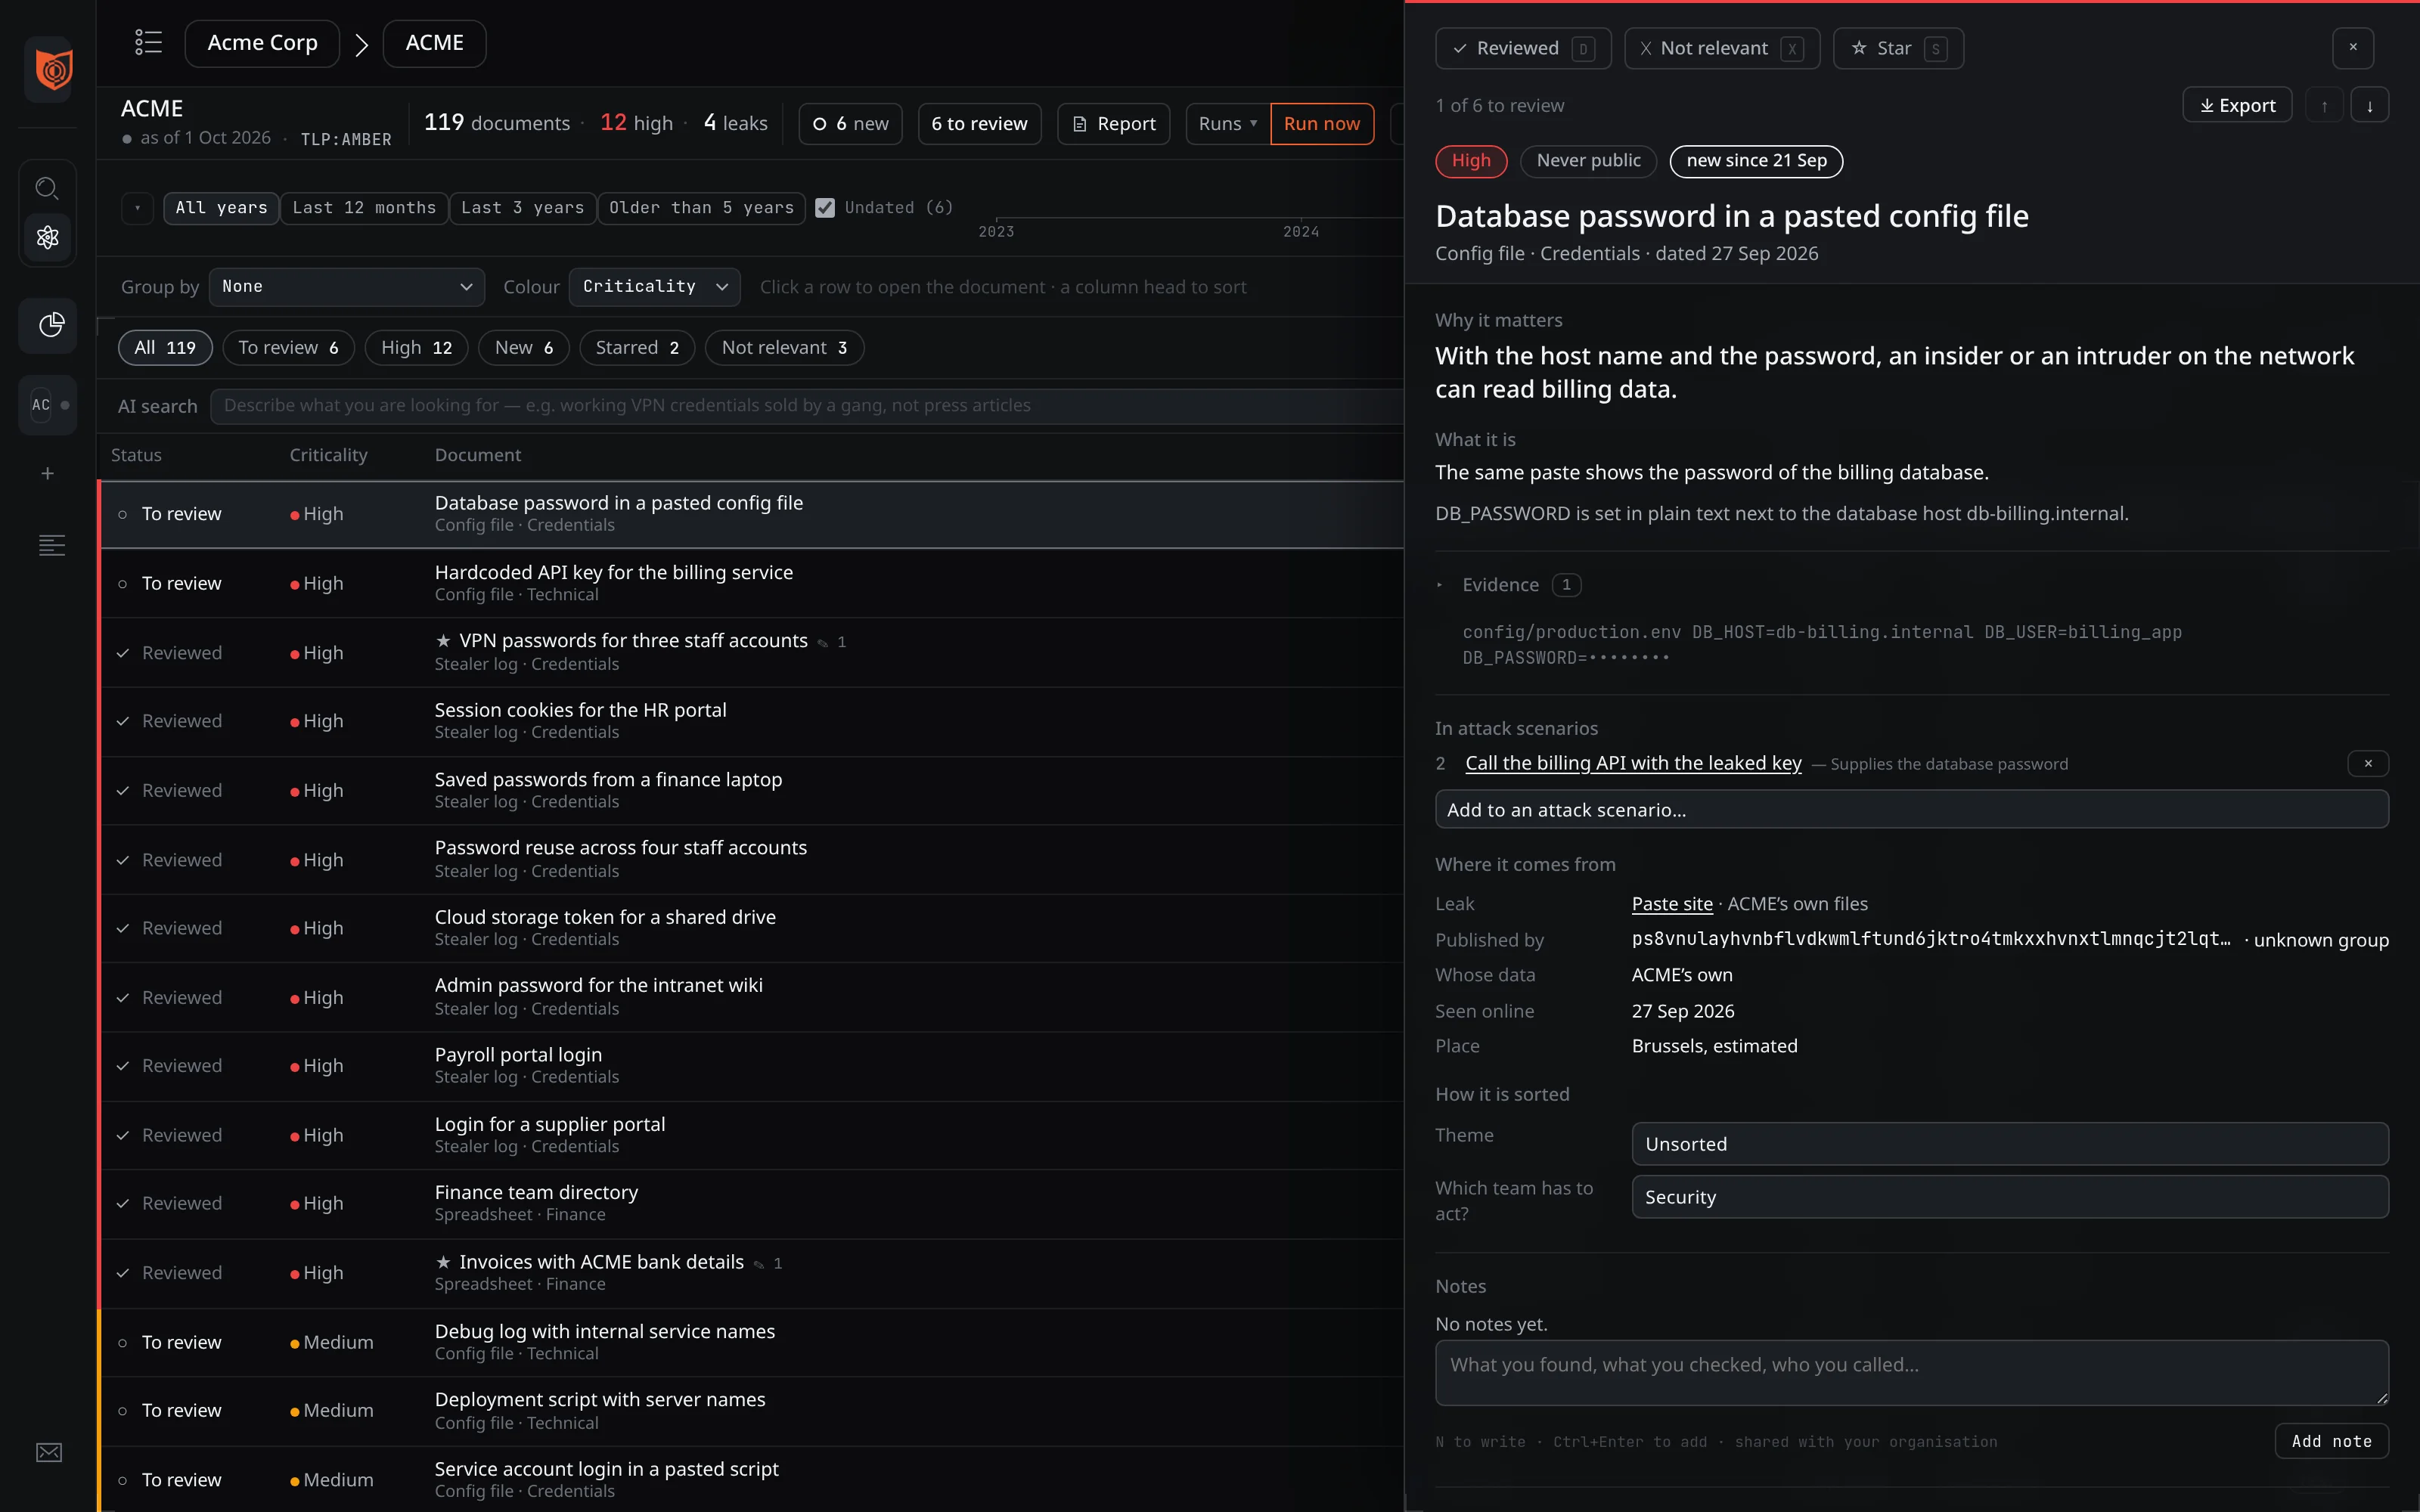
Monitoring, a document open · demo data
No one will ask you to read ransomware sites. Your clients, your insurer and the regulator will ask what leaked about you, and since when you knew. We agree with you what to watch and who receives what. After that, it takes almost none of your time.
Millions of files from one company and all its partners. One line is yours. We point to it.
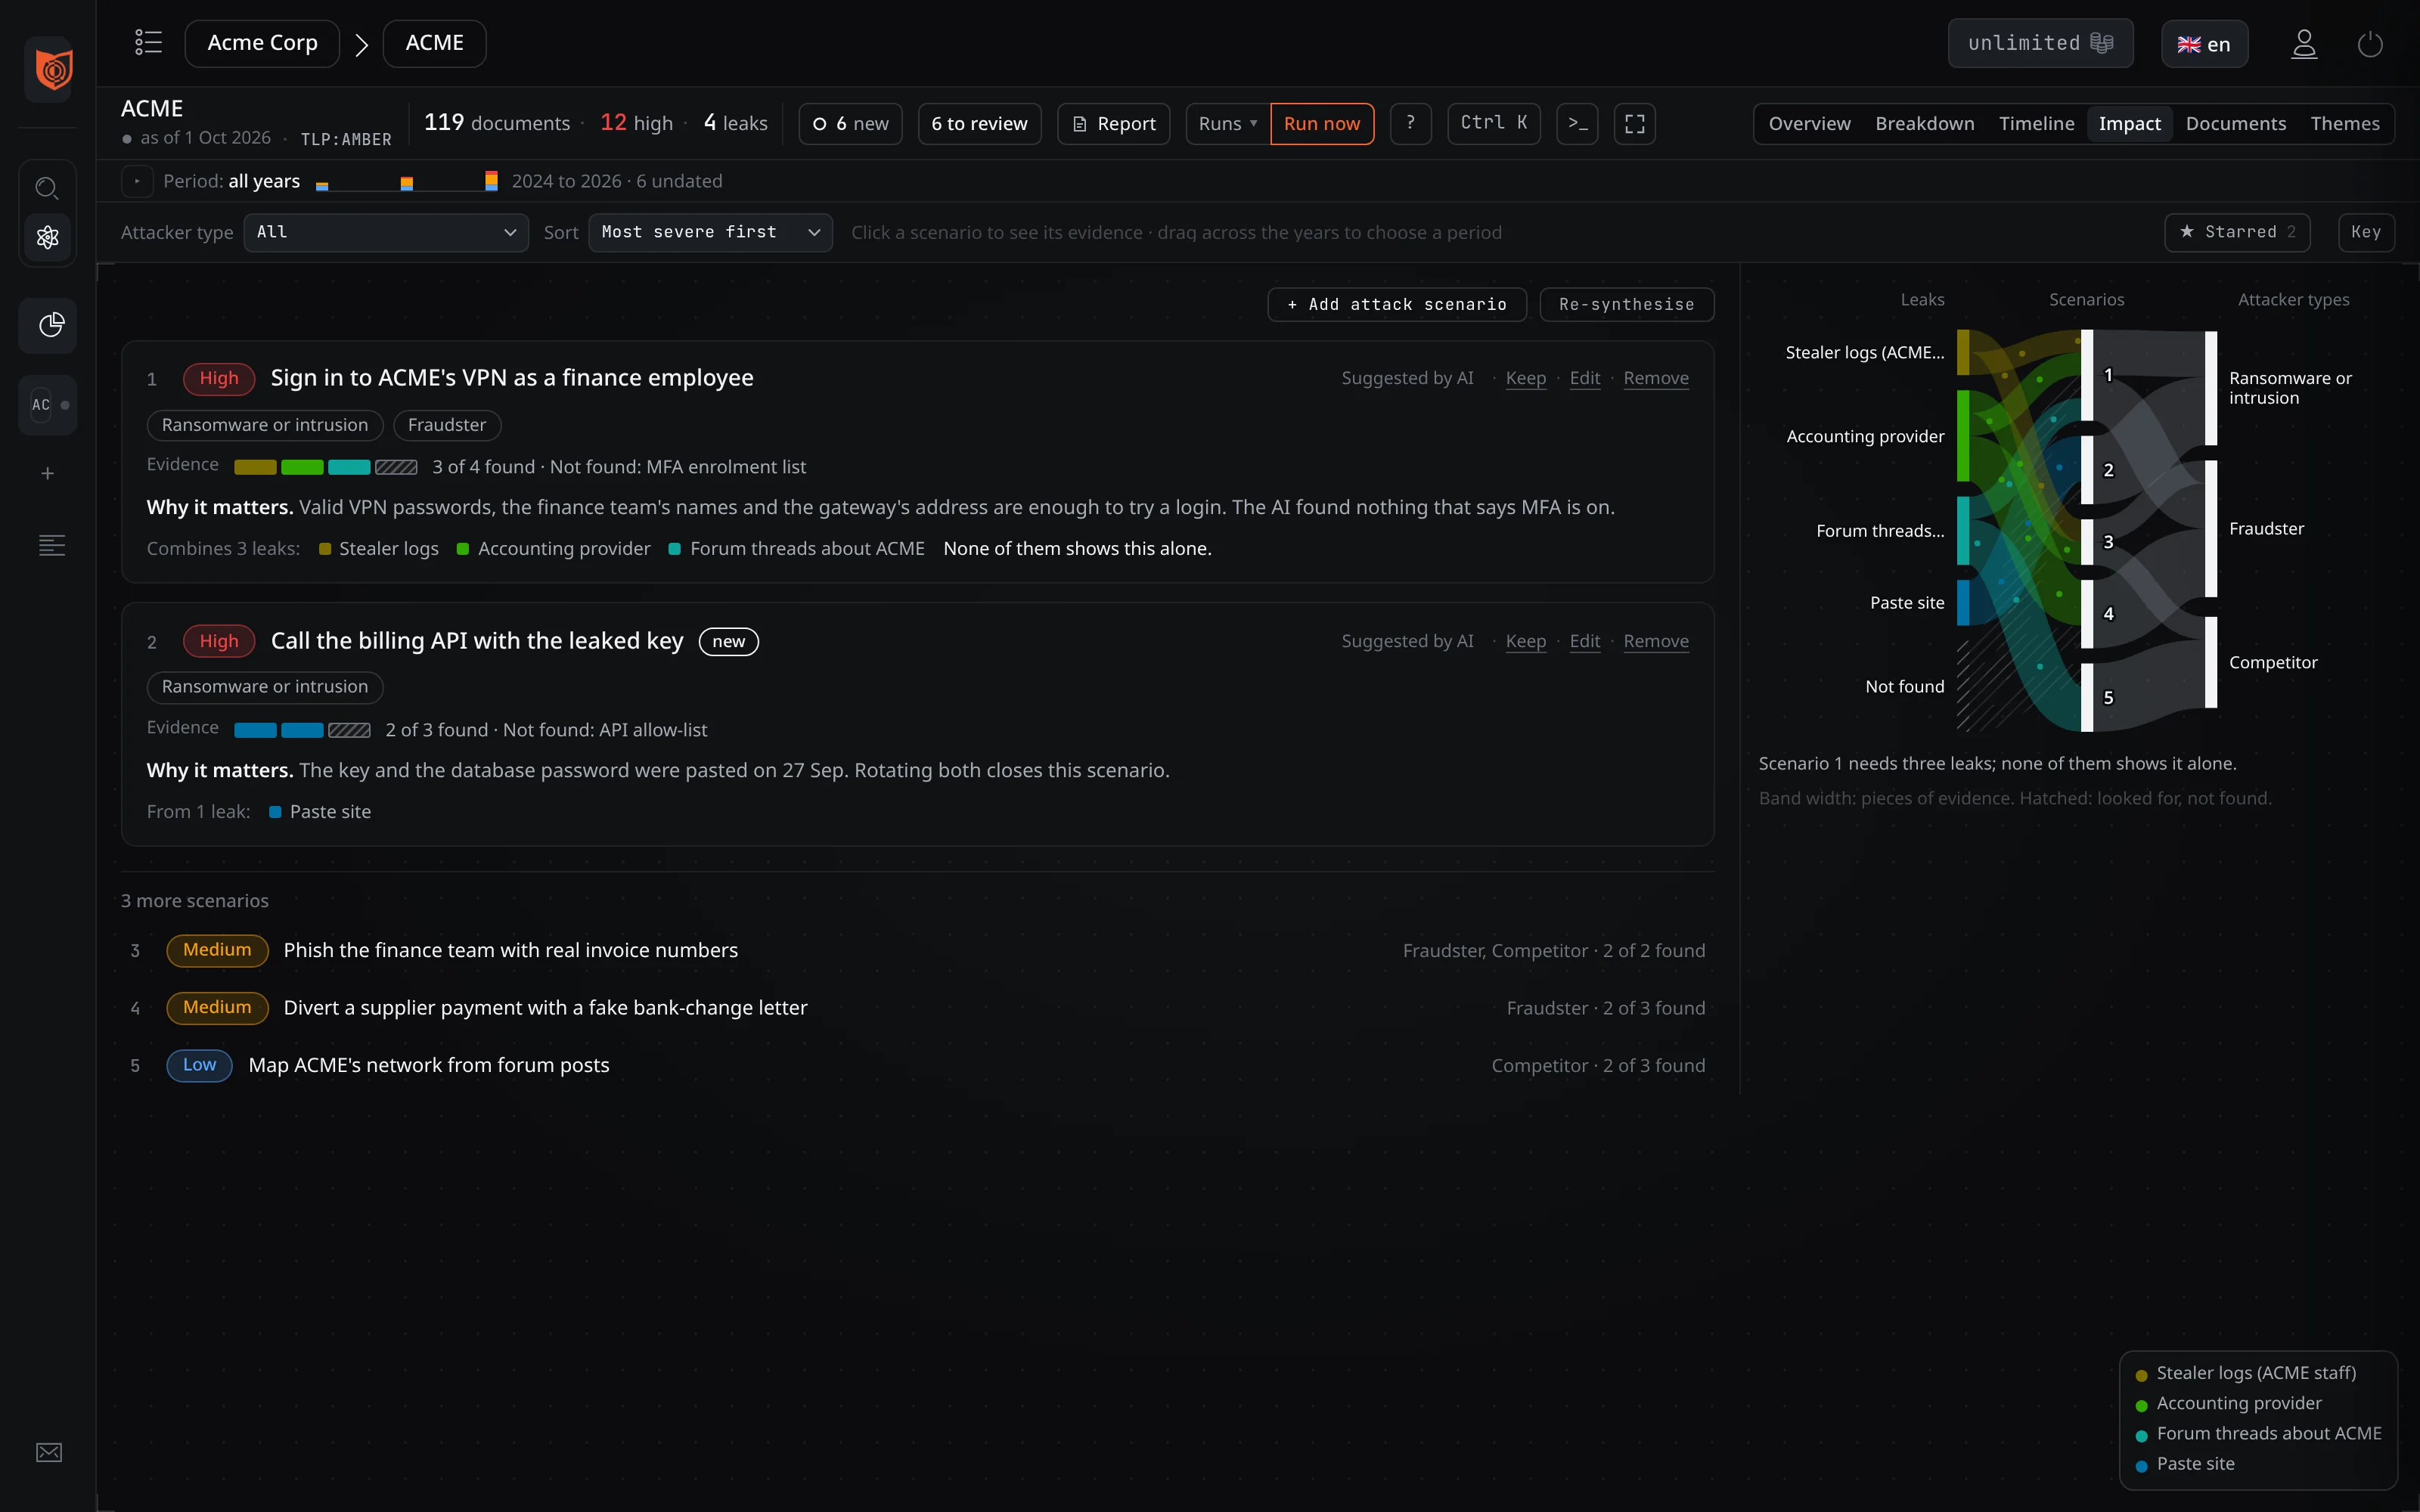
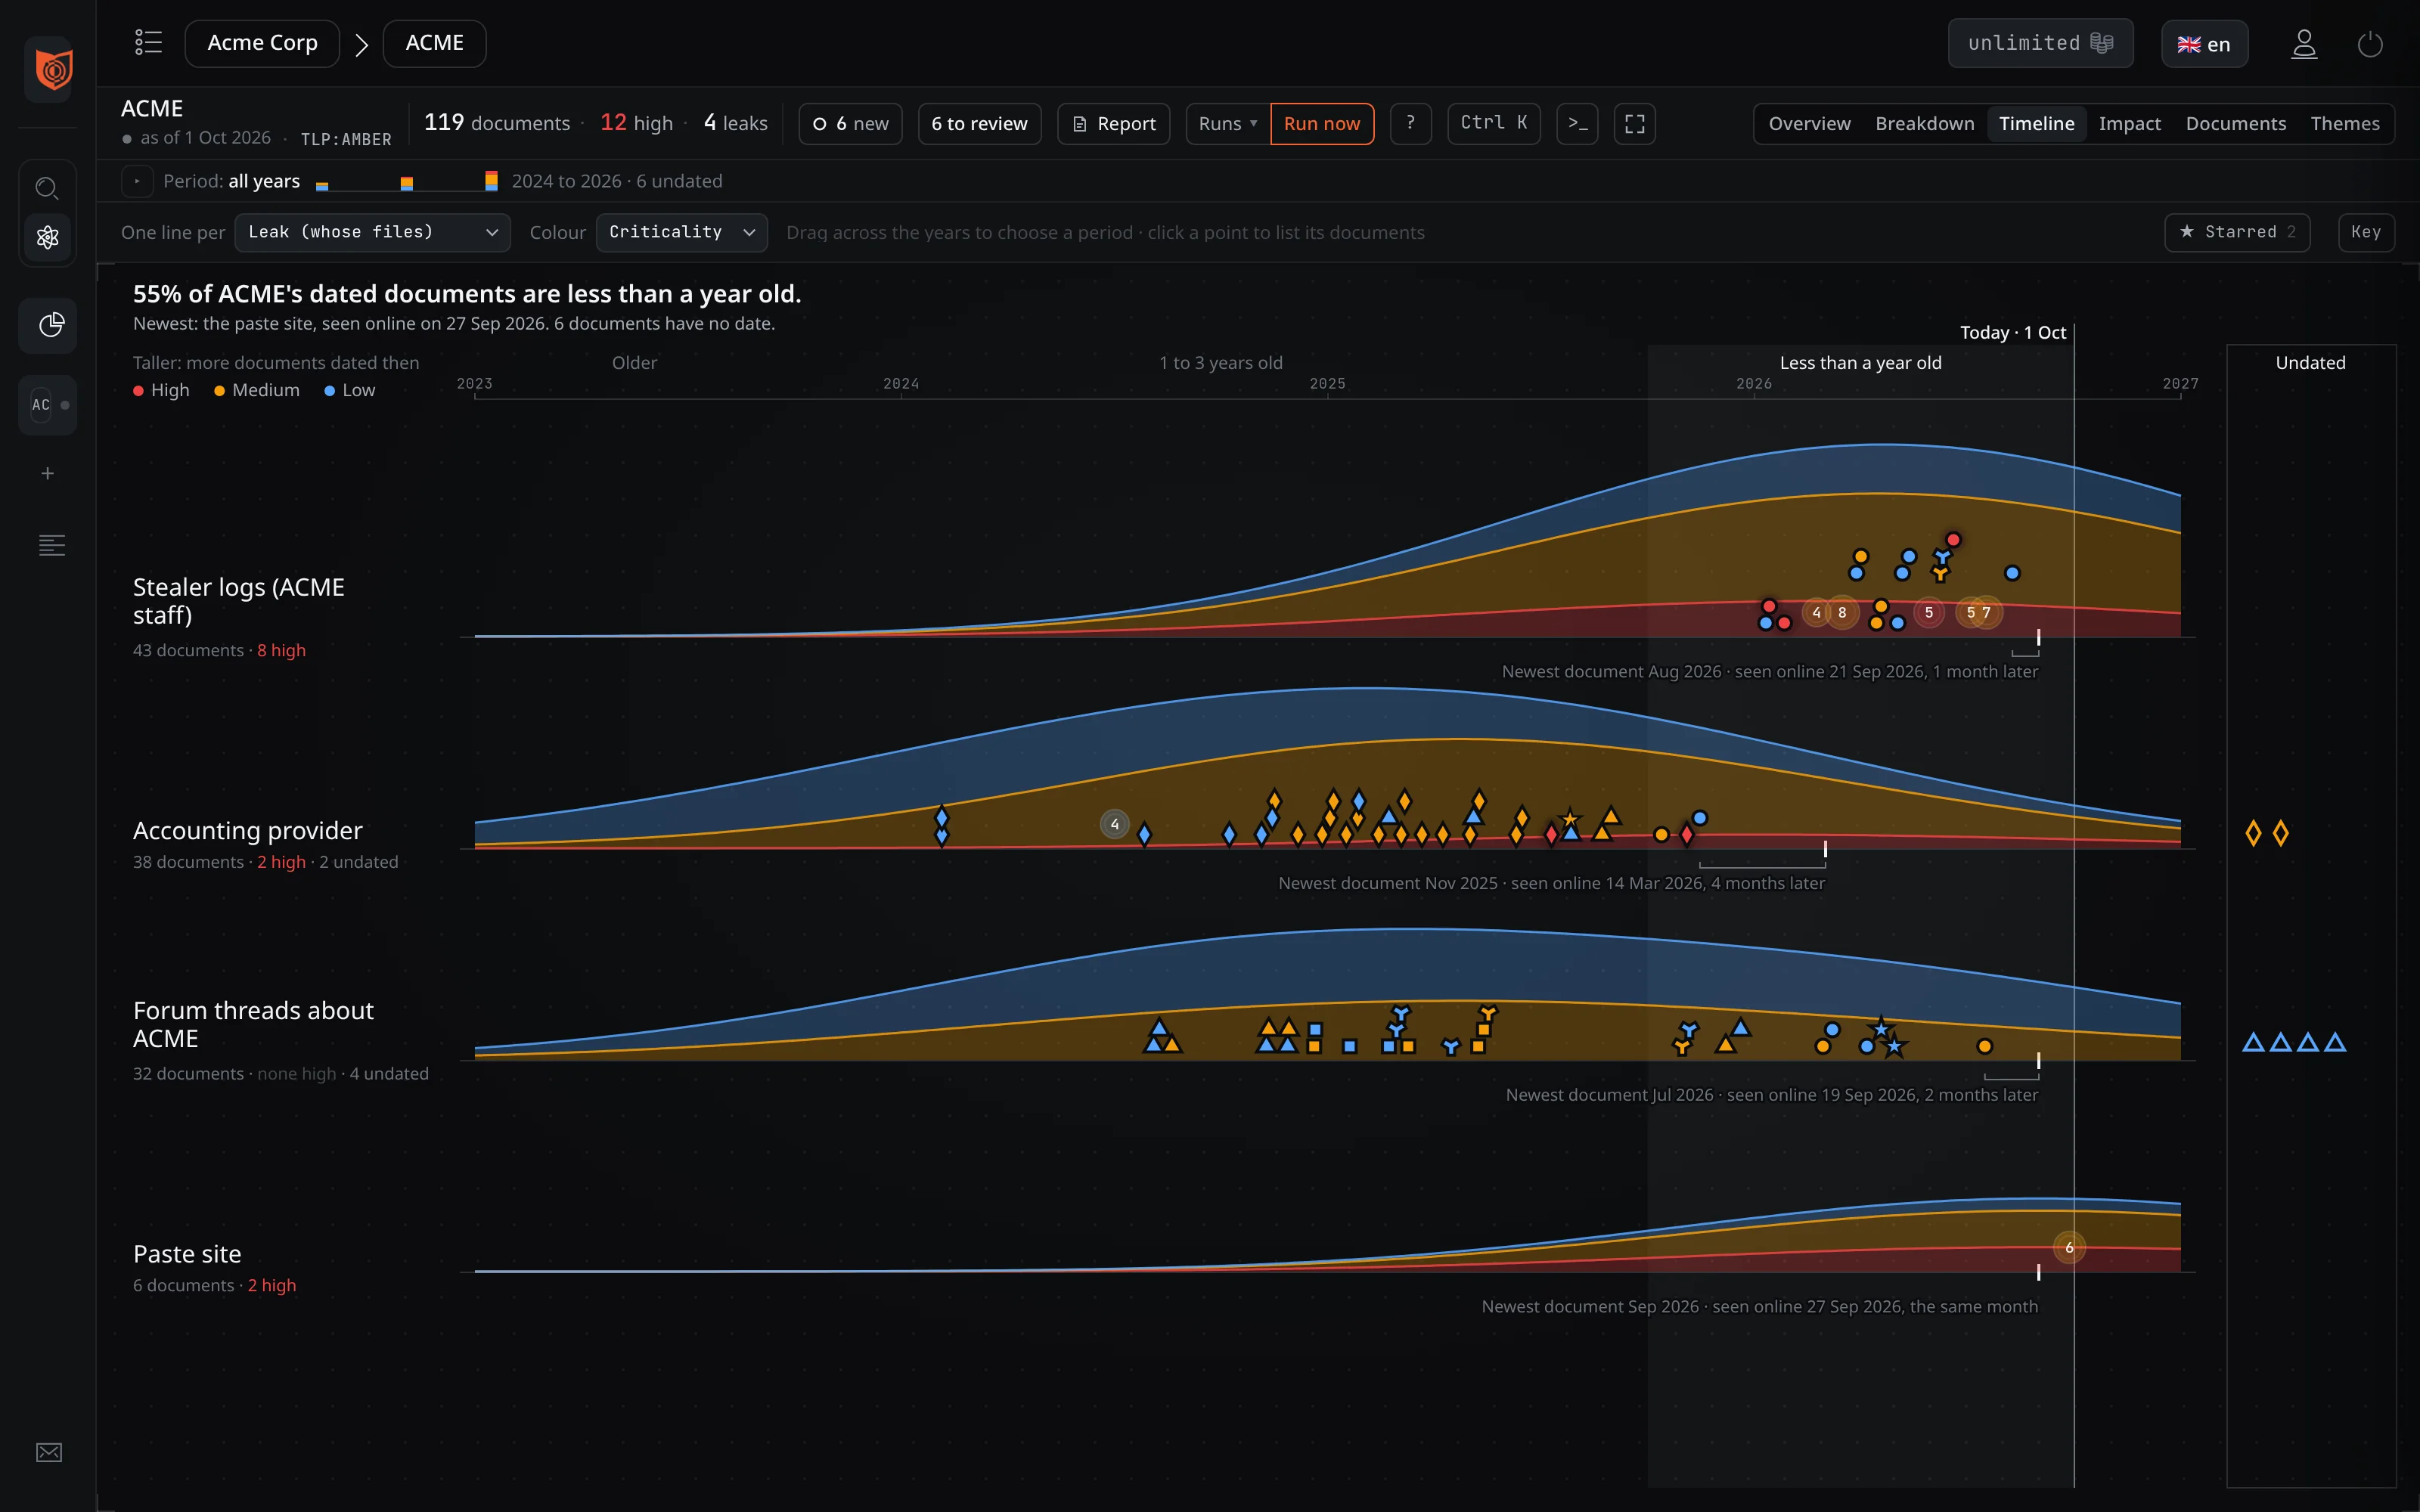
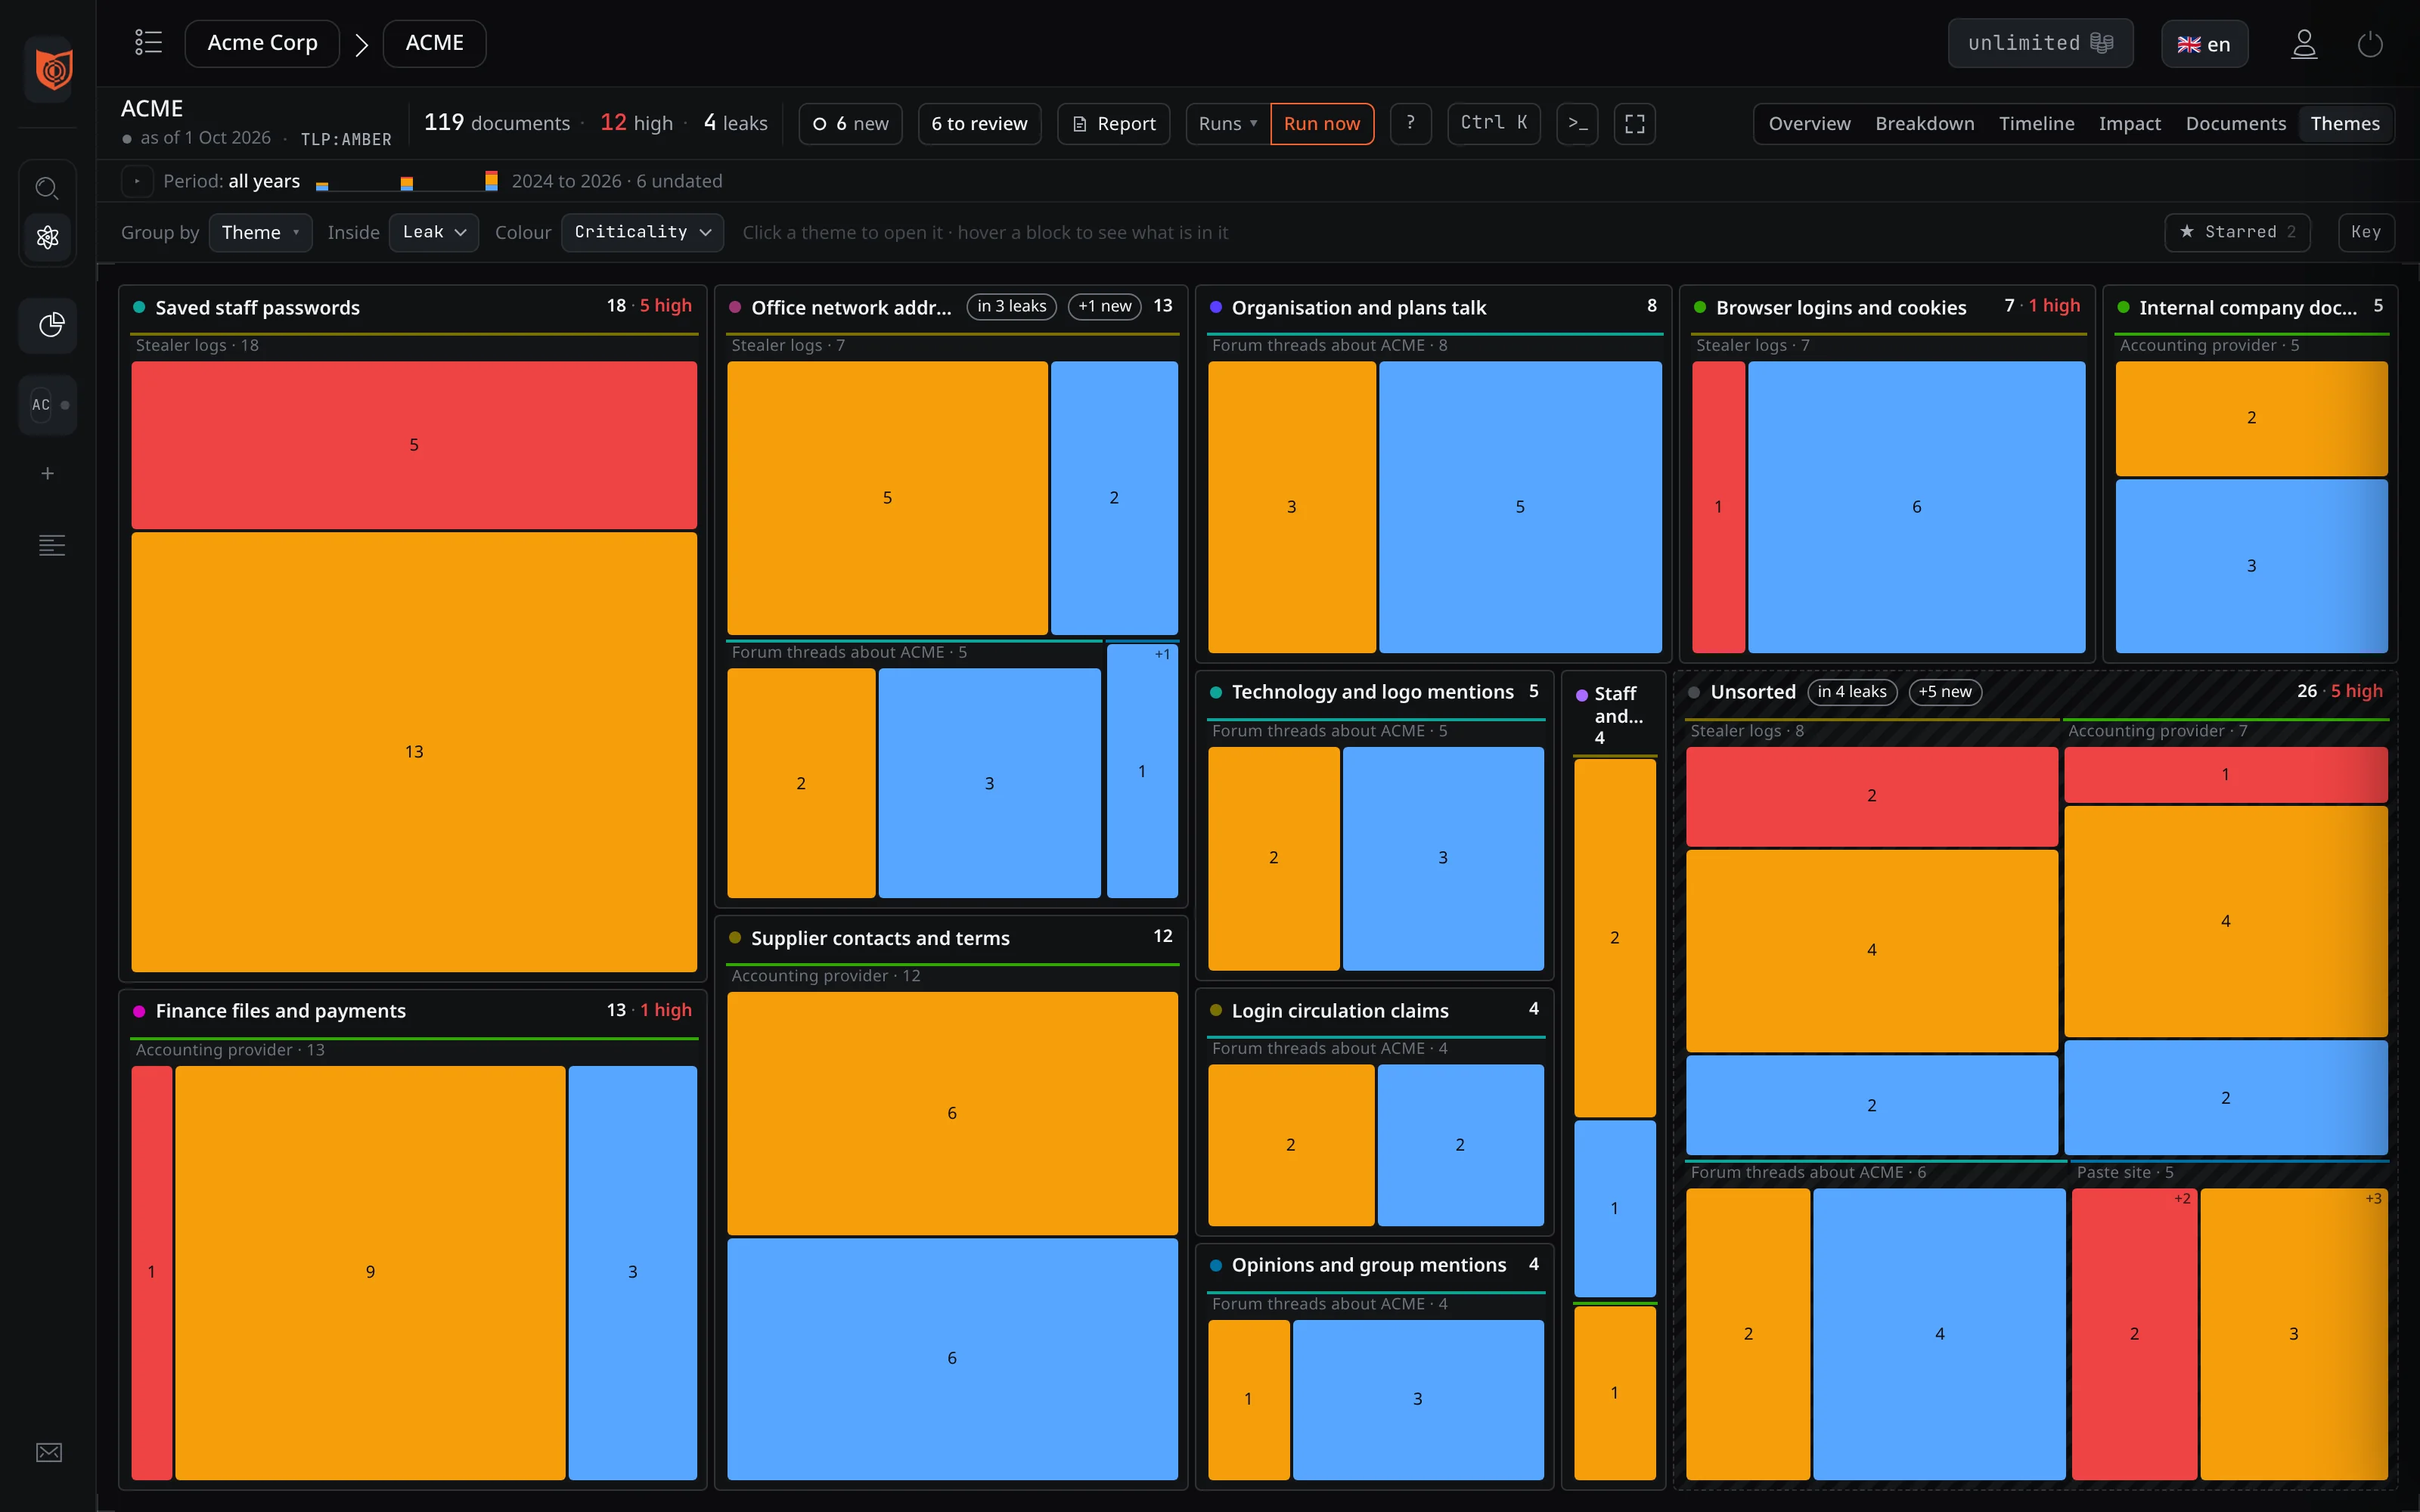
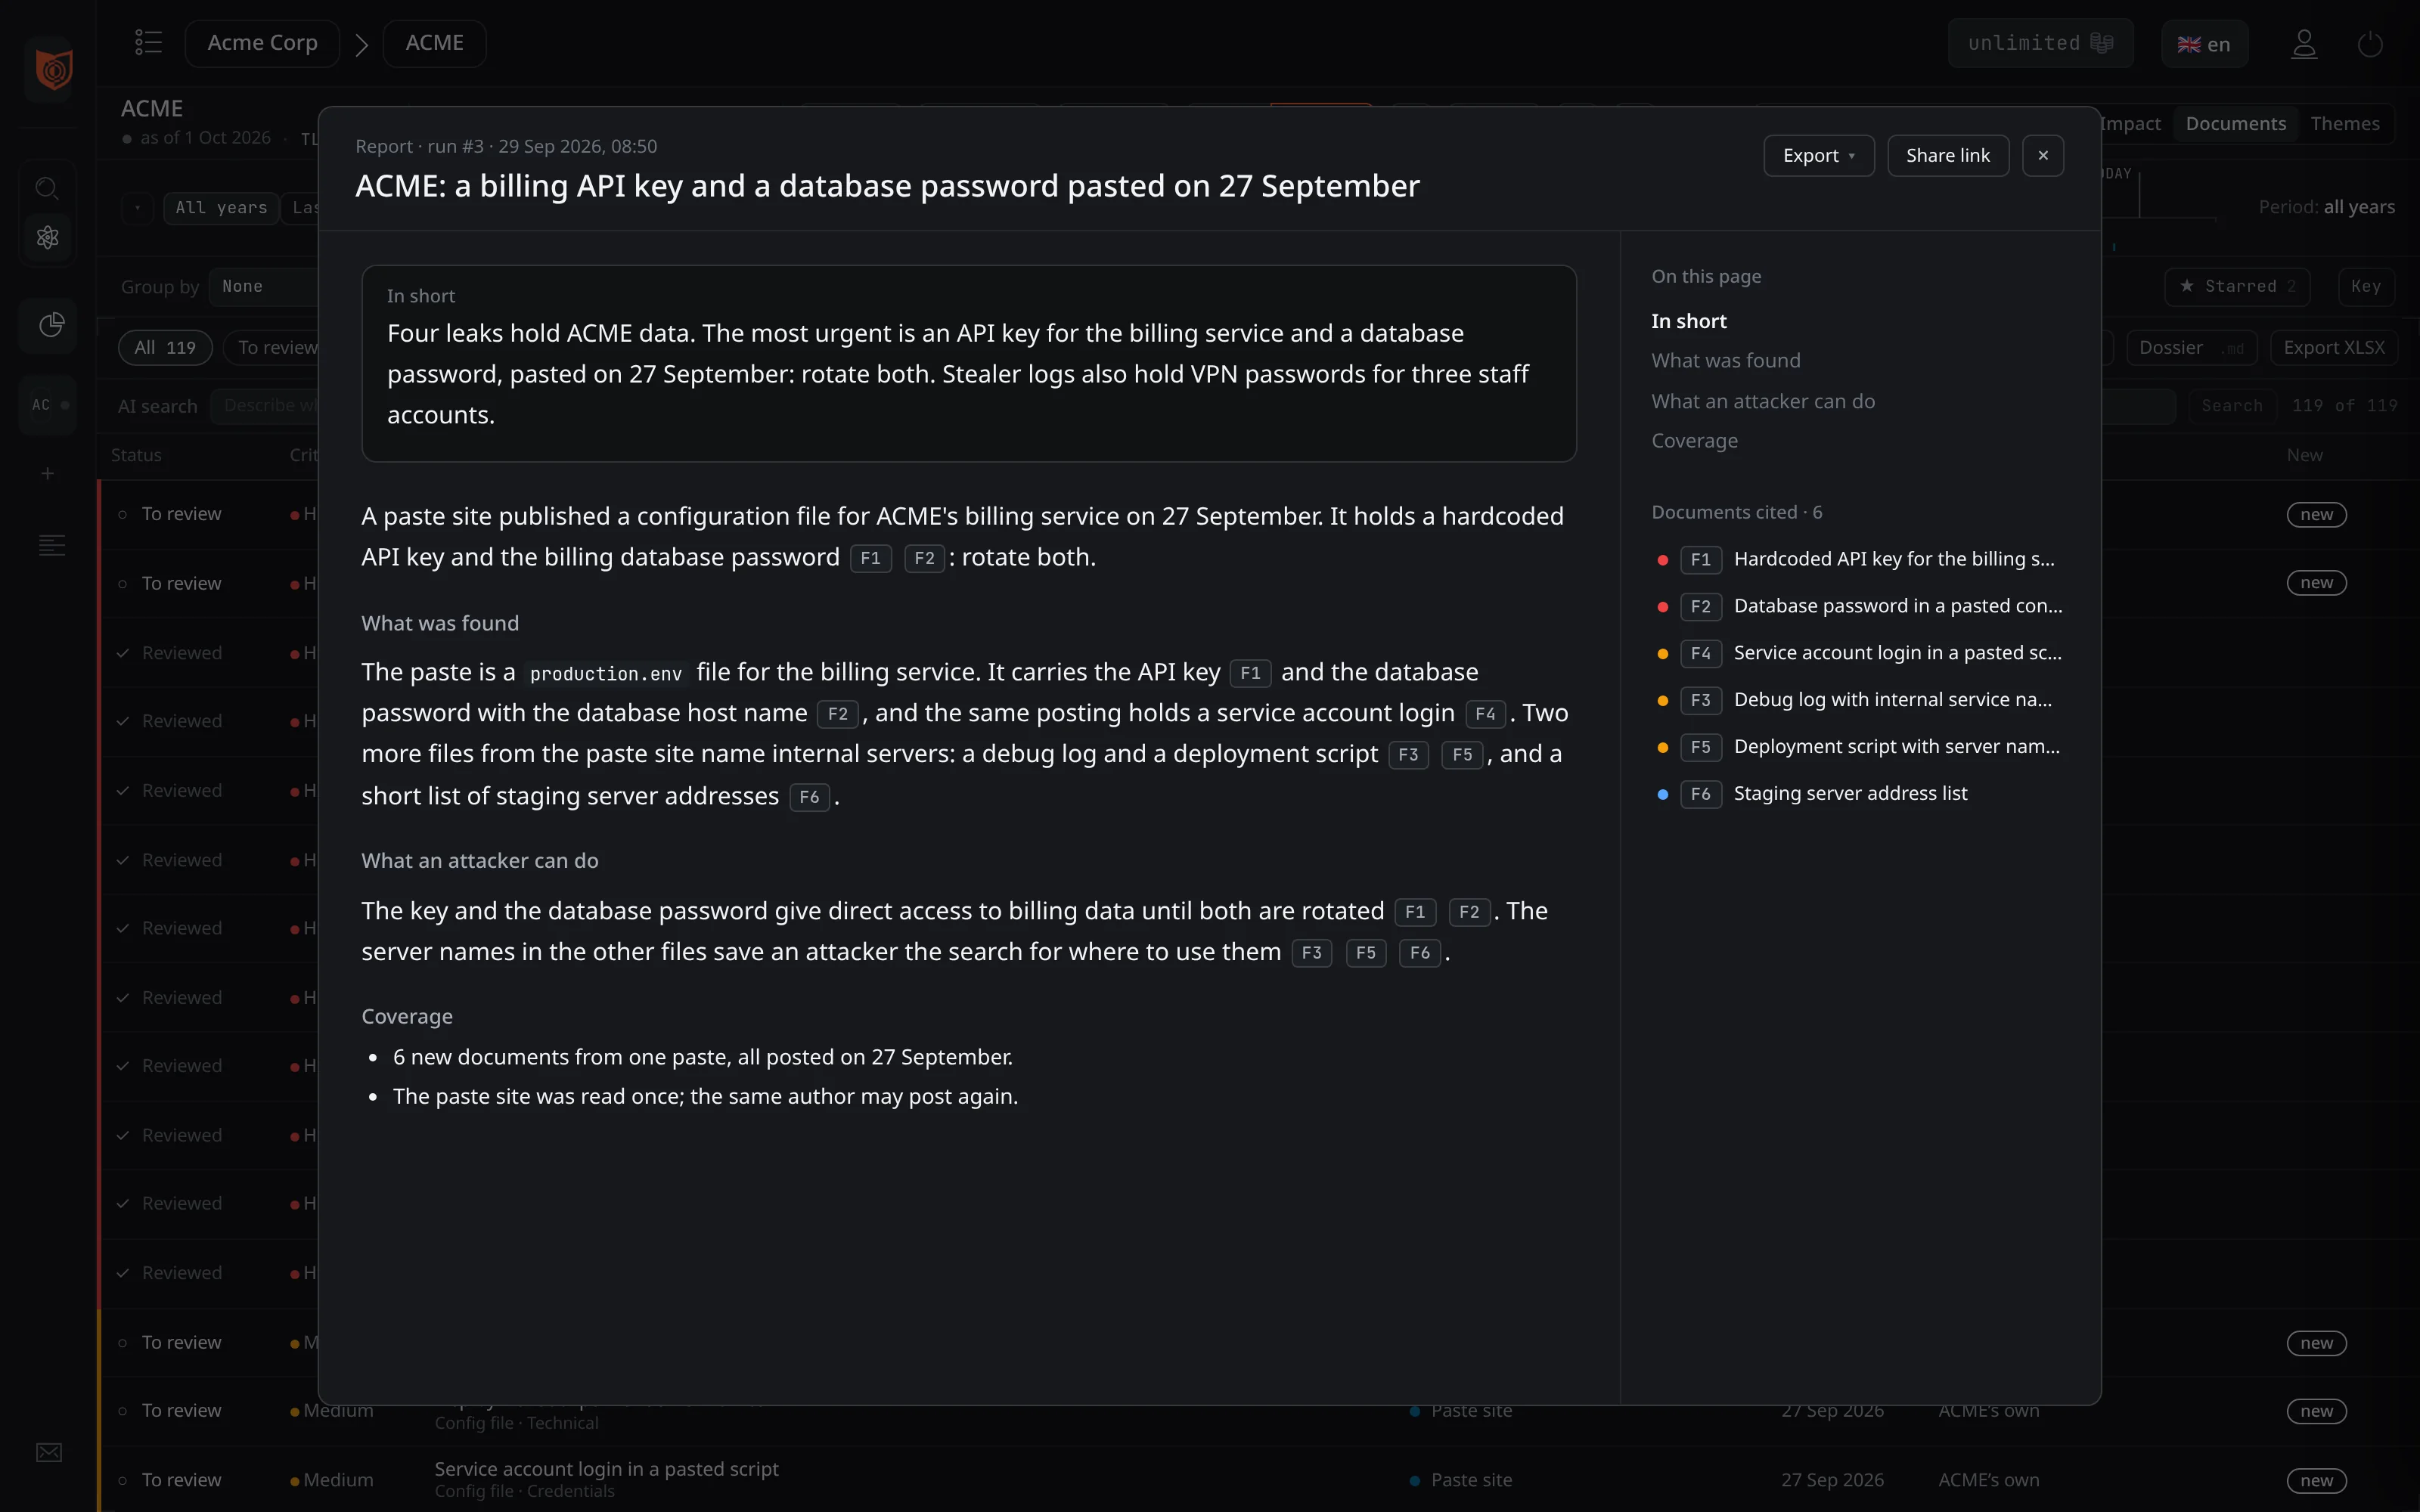
What an attacker can do with what leaked. Scenario 1 needs three leaks. A watch on your name misses it.
How old the documents are, and when they surfaced. Here, more than half are under a year old.
The documents by theme. Each department sees its own.
The report, in short first. Made to be forwarded.
Monitoring, Impact · demo dataKeys shown as in the app
Every document of every published leak. A part number, a programme, a domain. Logged by no one.
Sold on its own, or included with Monitoring.
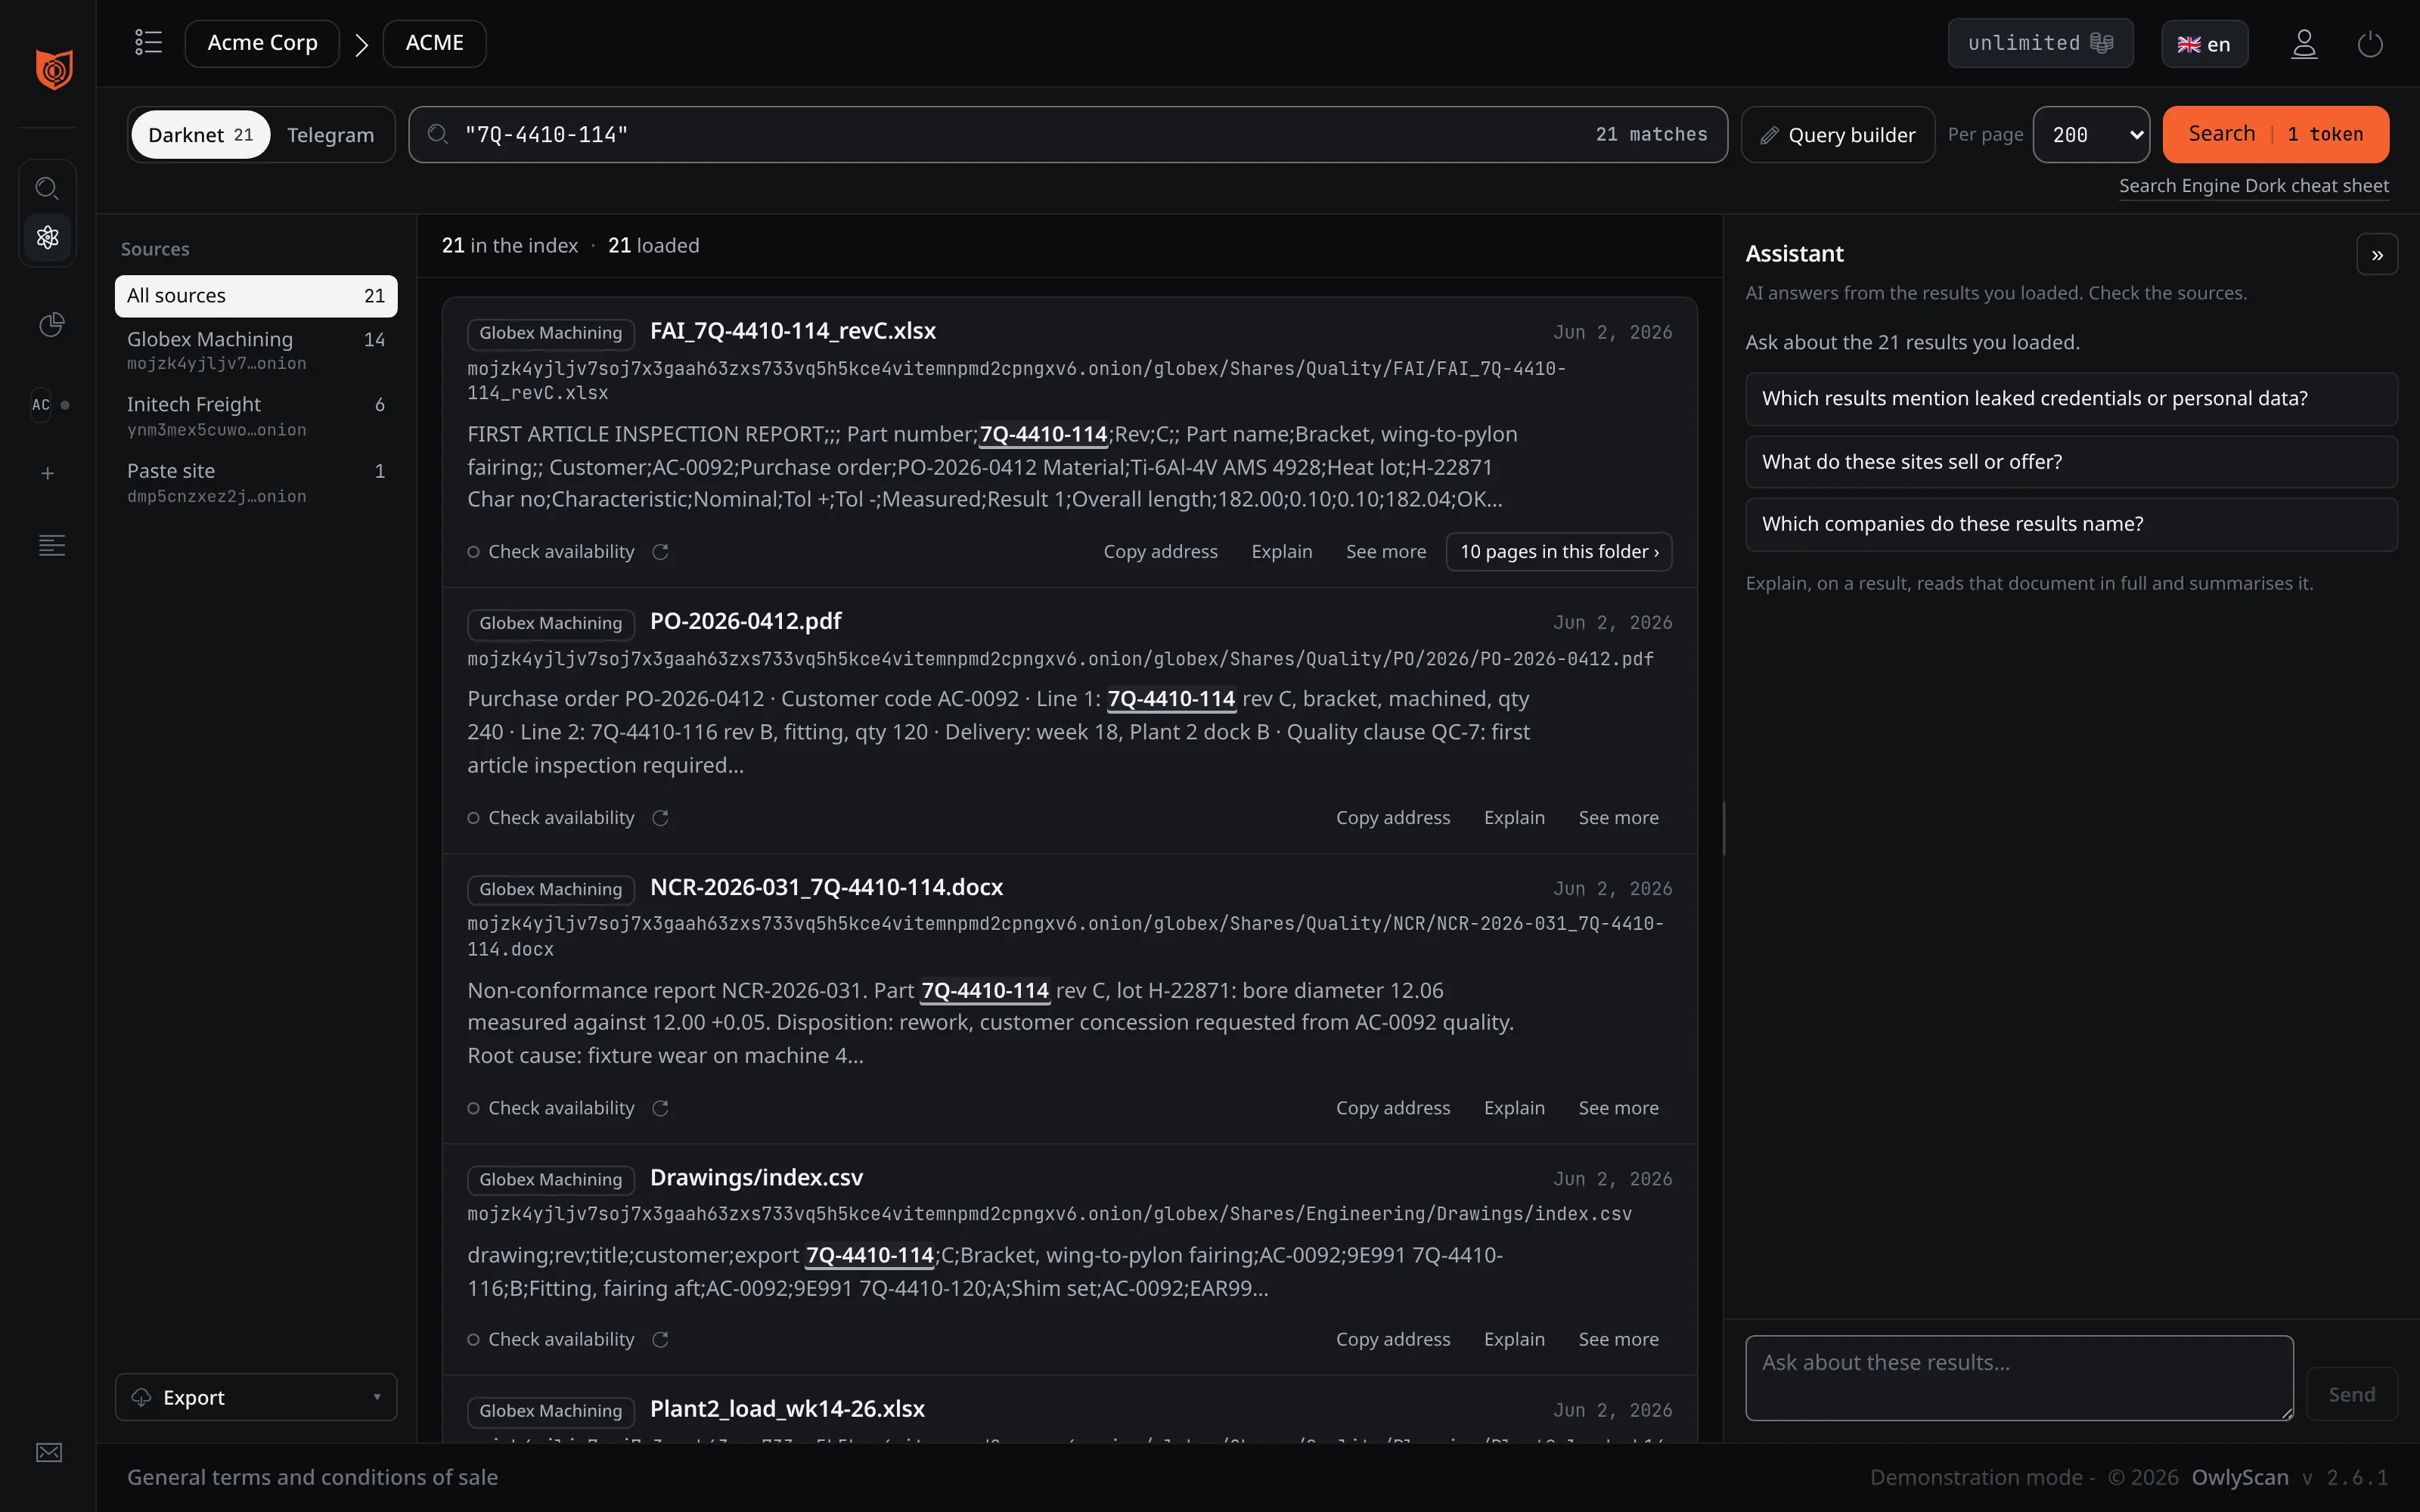
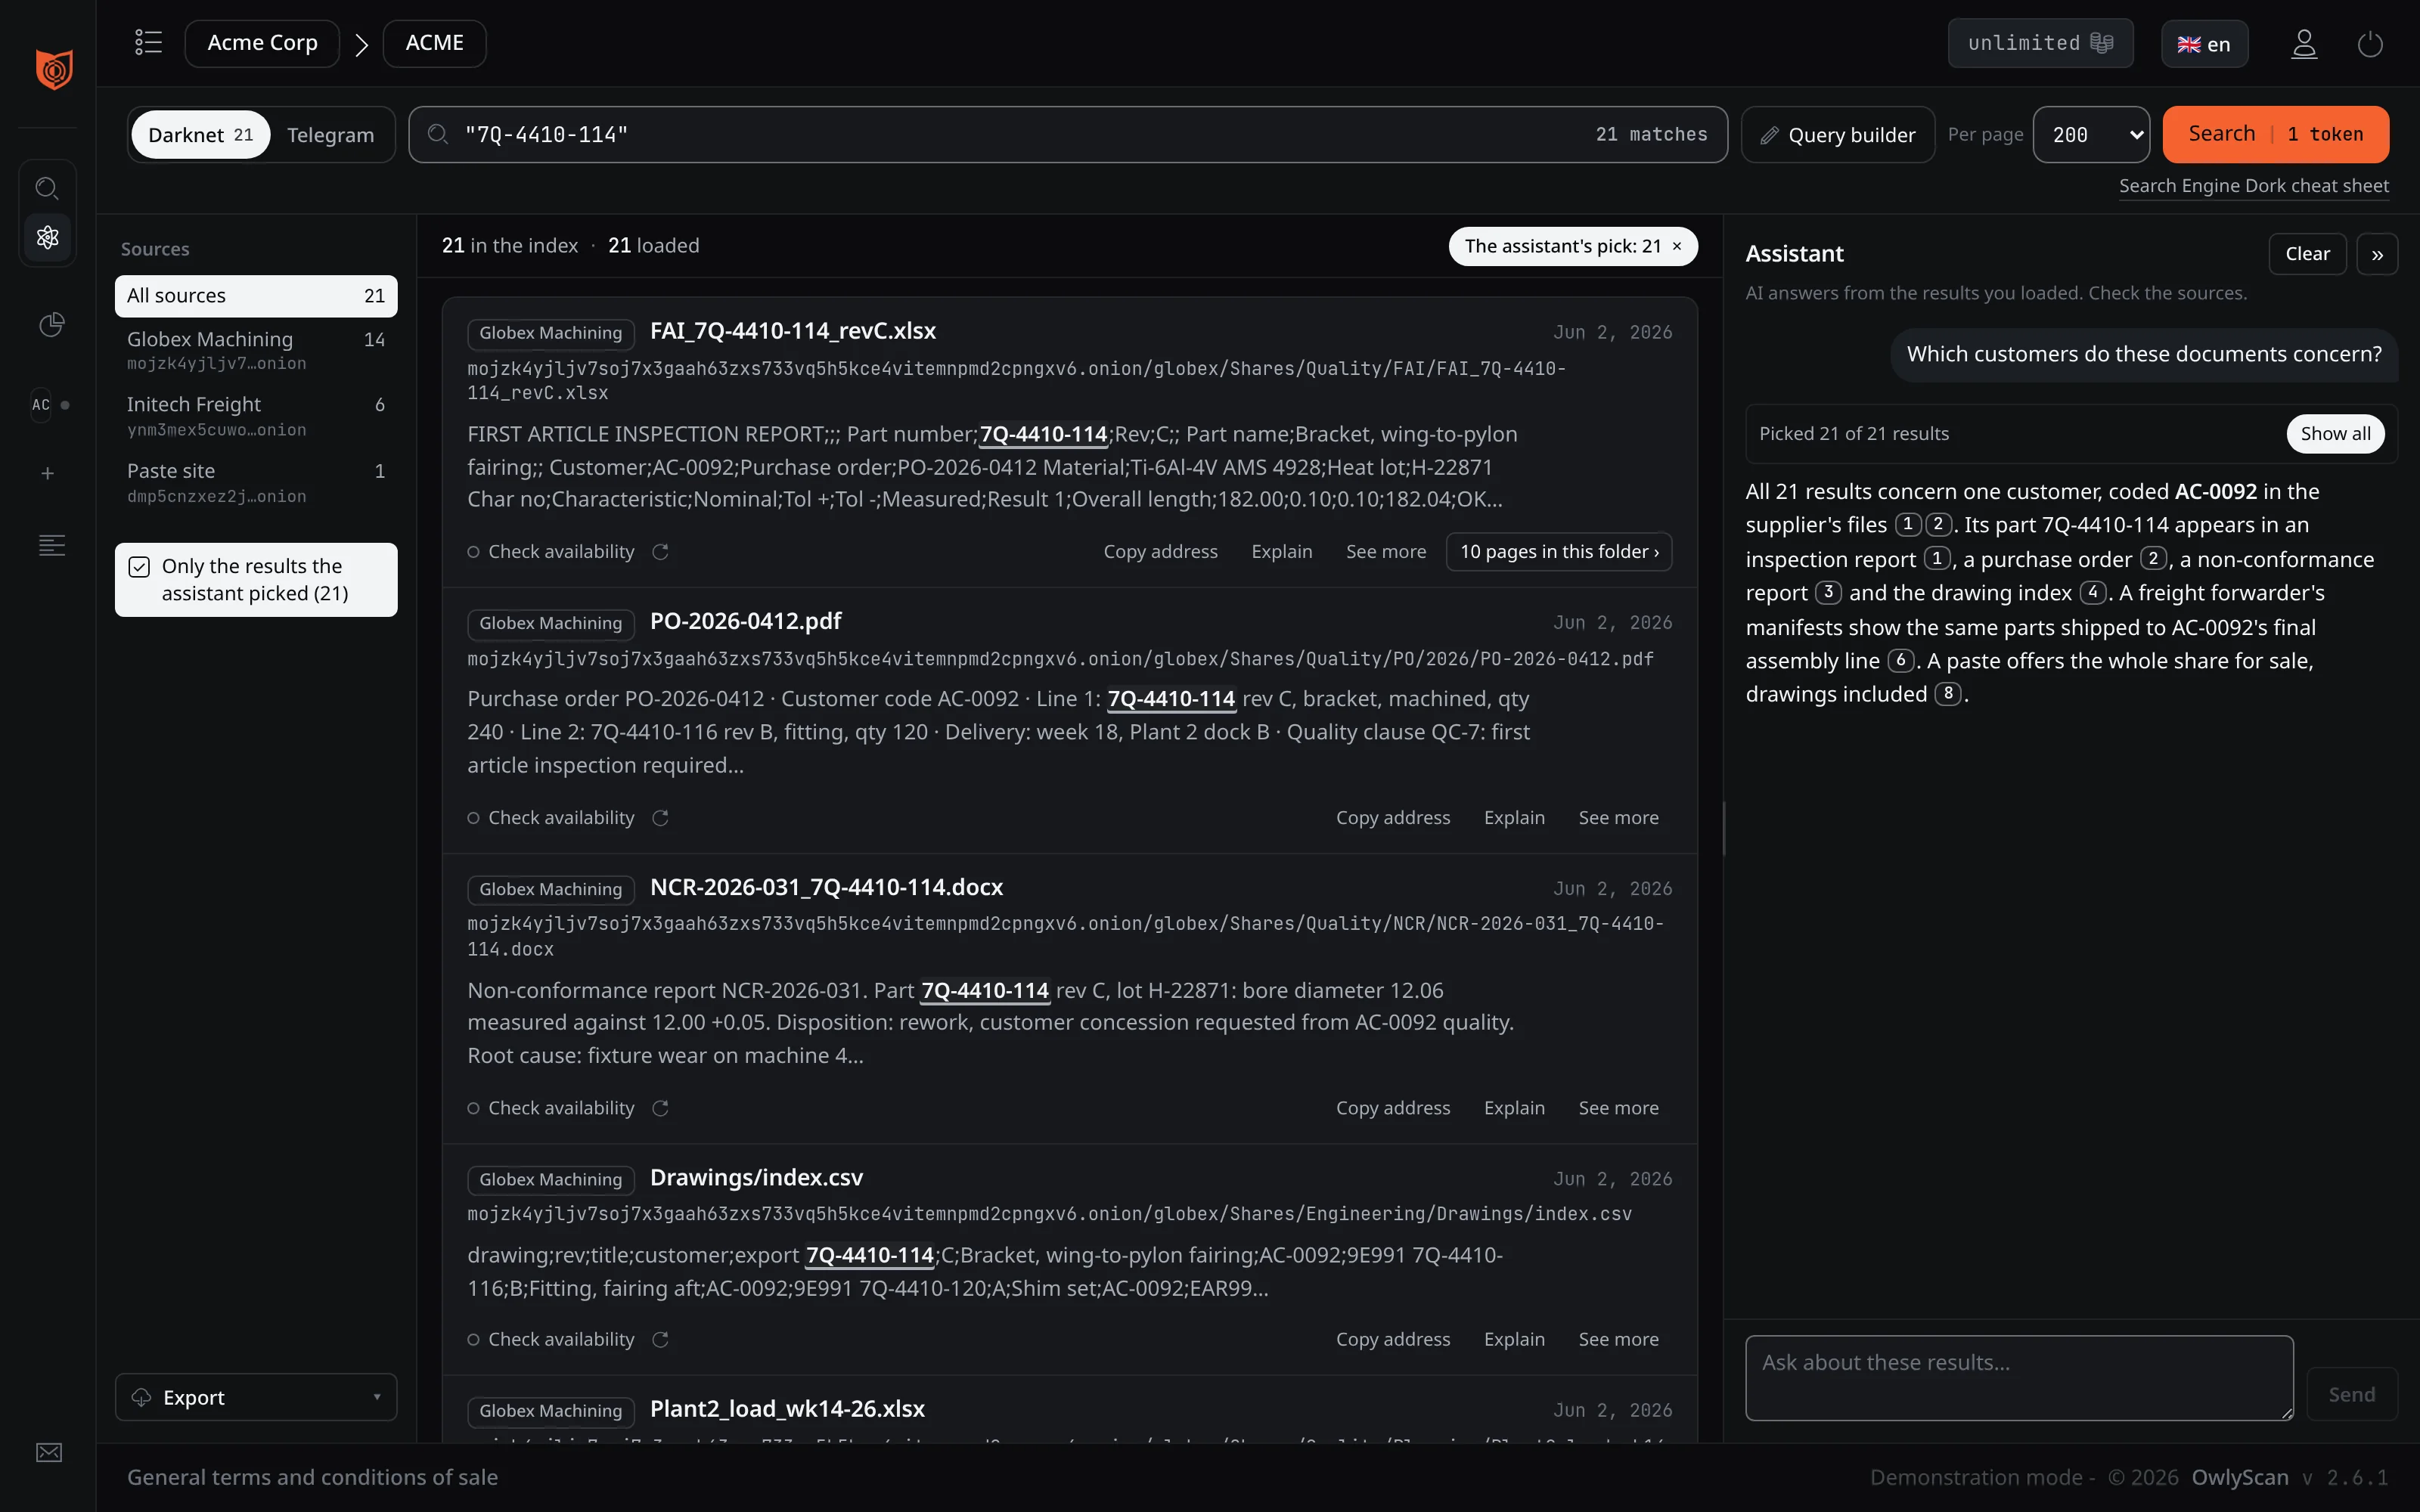
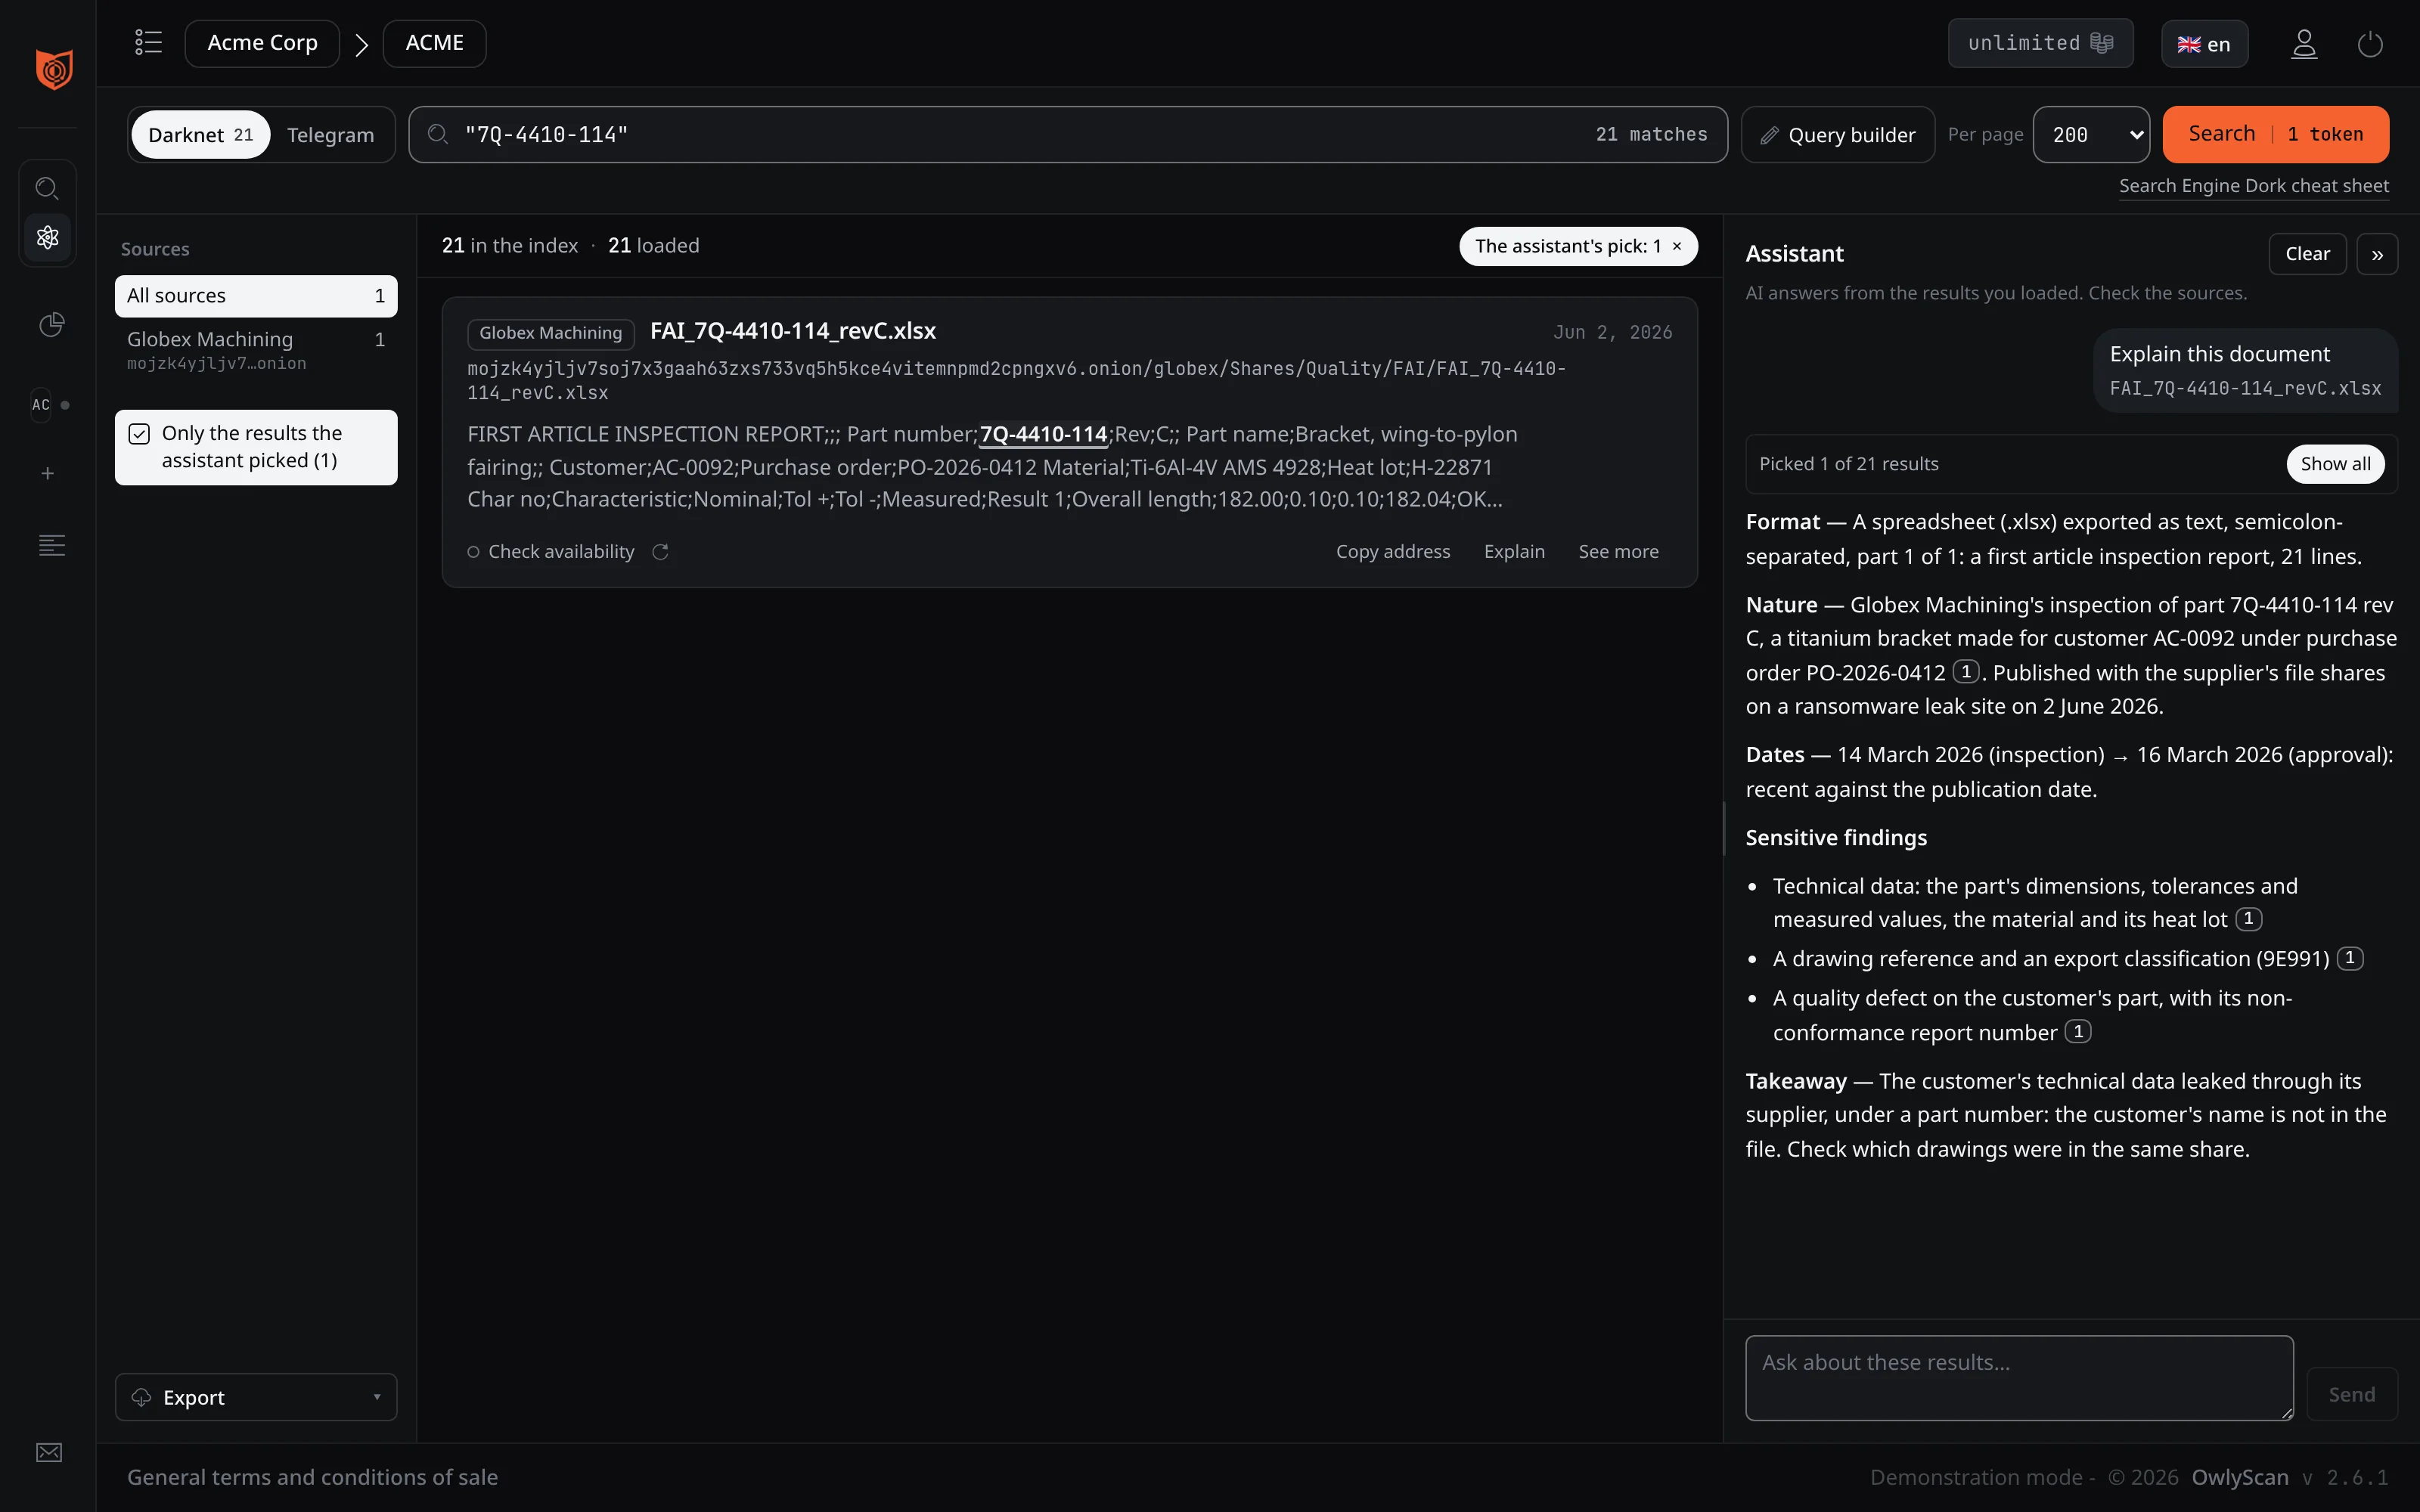
A part number, not a name. 21 documents in two supplier leaks and a paste, grouped by folder, the term marked in each passage.
Ask about the results you loaded. Every answer cites the results it comes from, and keeps on screen only the ones it used.
Explain reads one document in full. Its format, what it is, its dates, what is sensitive in it, and what to take away.
Investigation, keyword search · demo data
Formatted by the AI
Headings and tables, without changing a value. The raw text stays one tab away, to check it against. One click, one search.
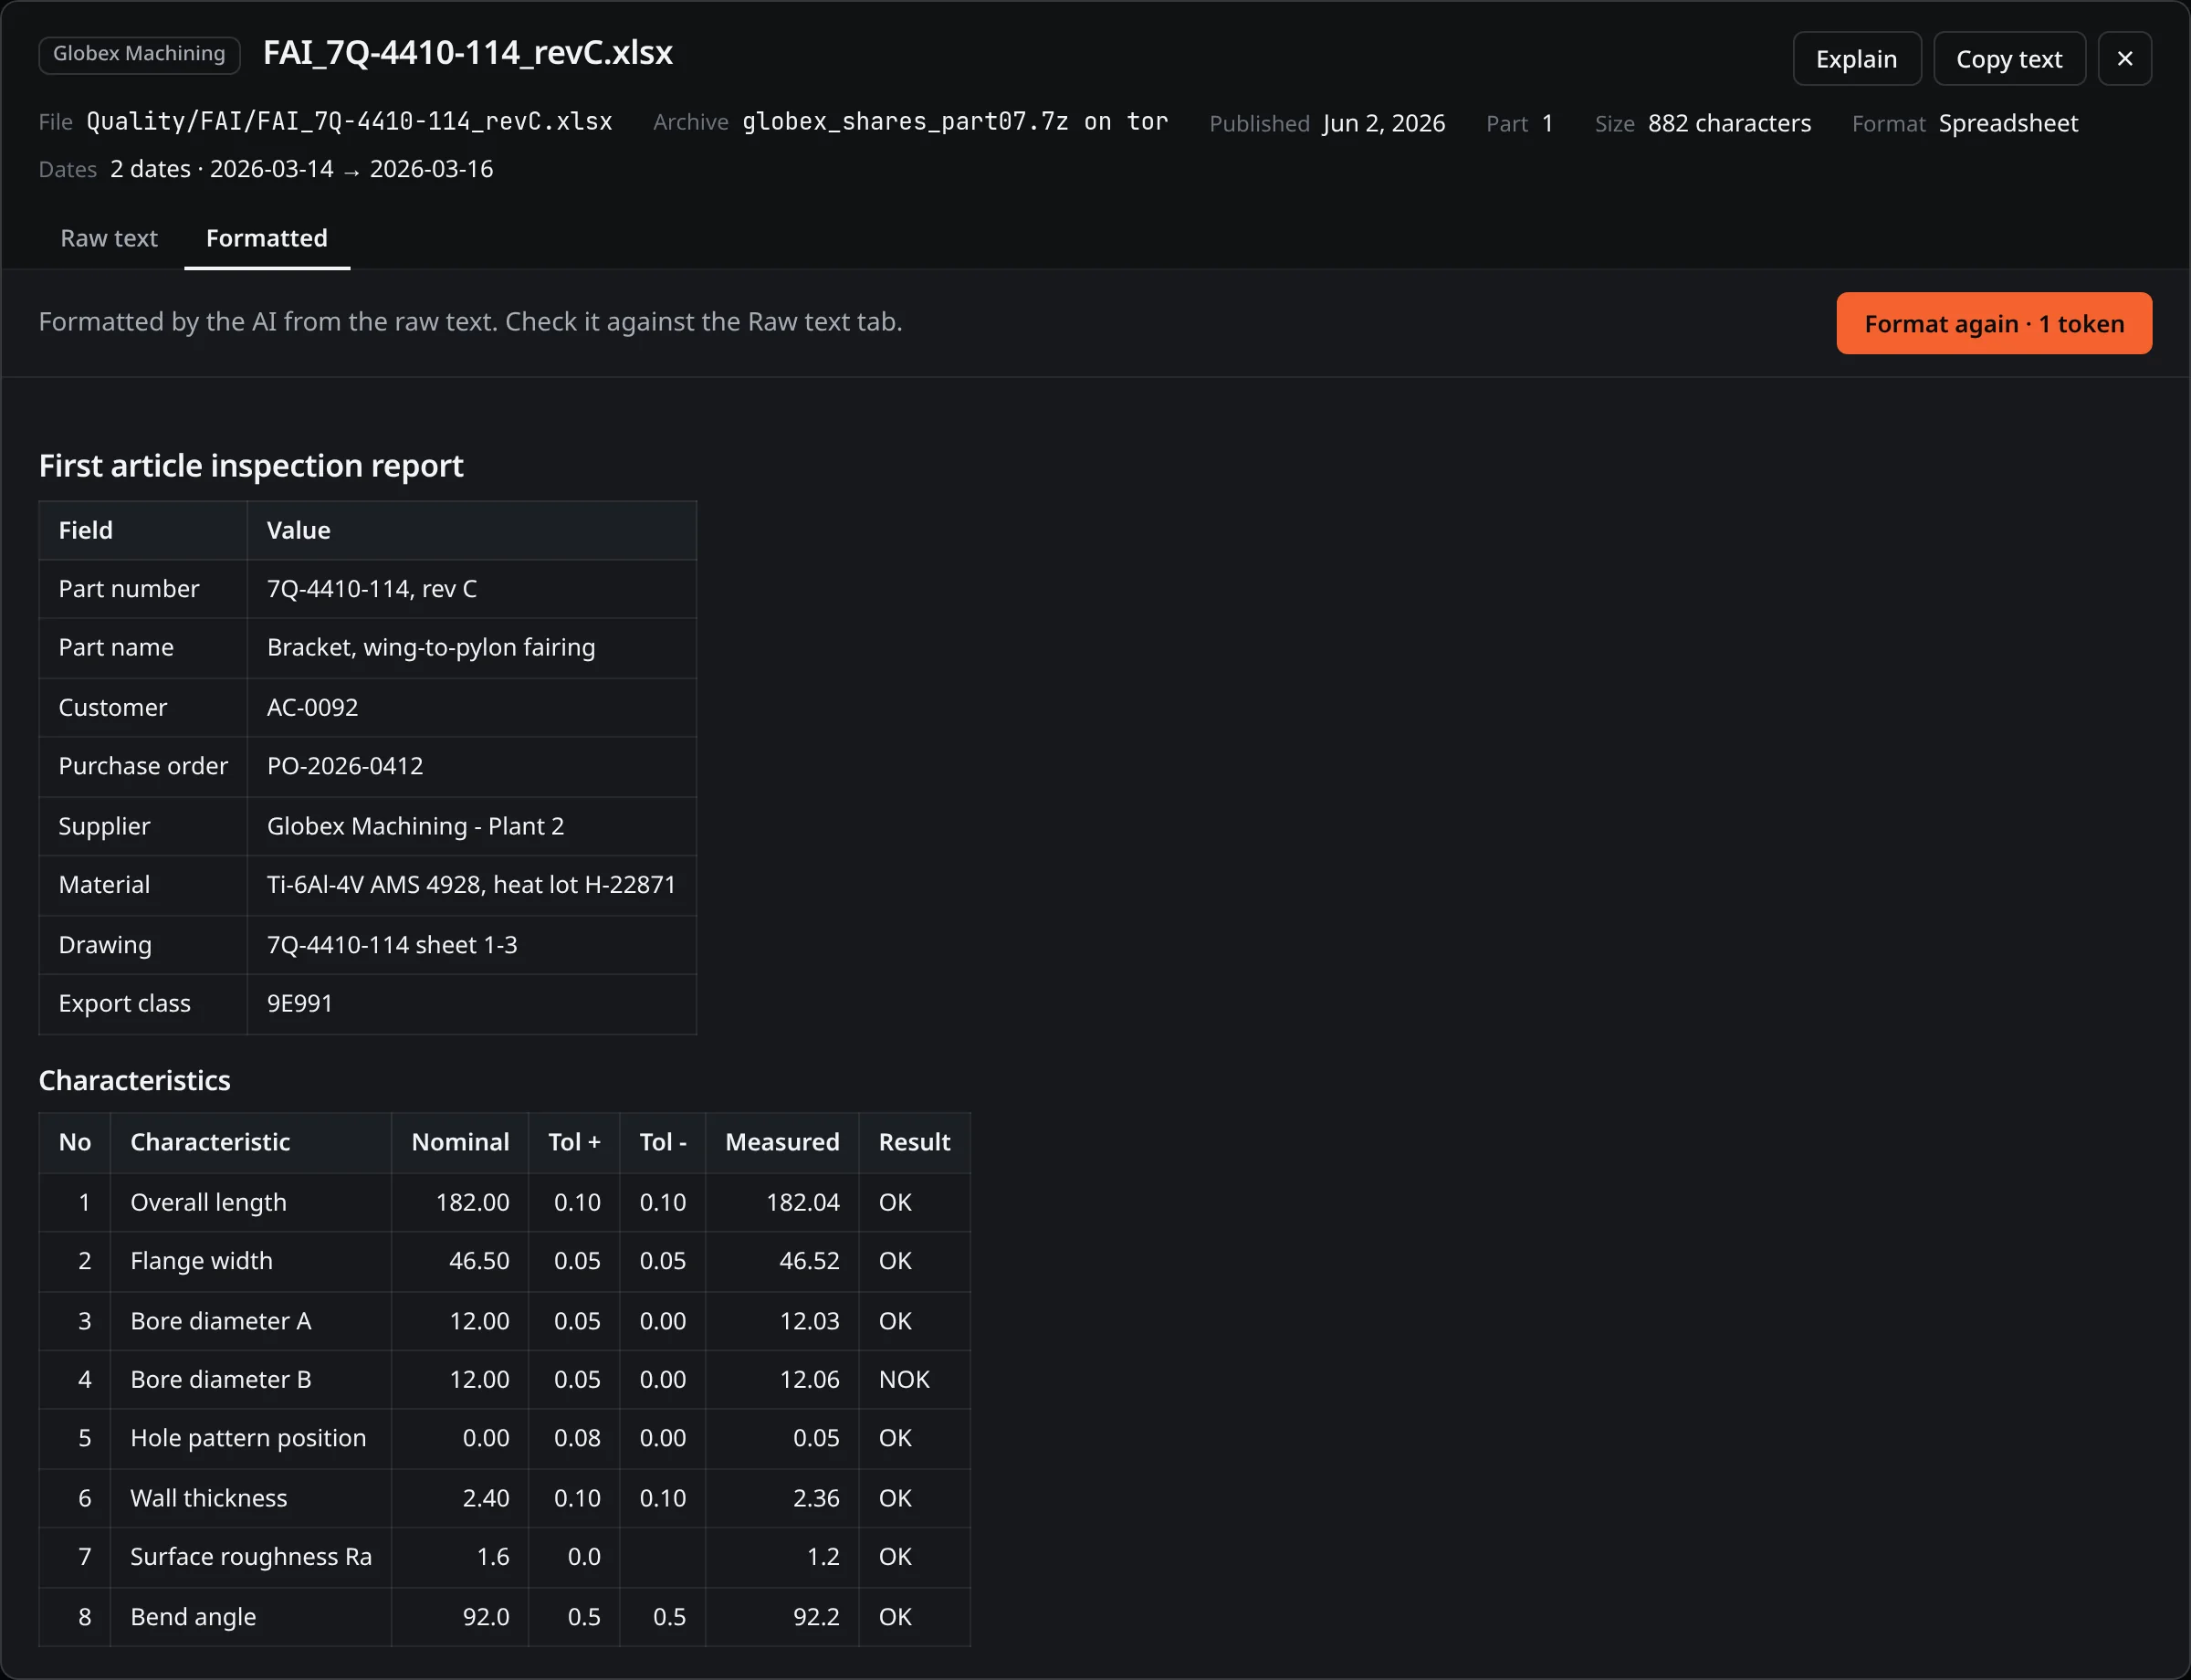
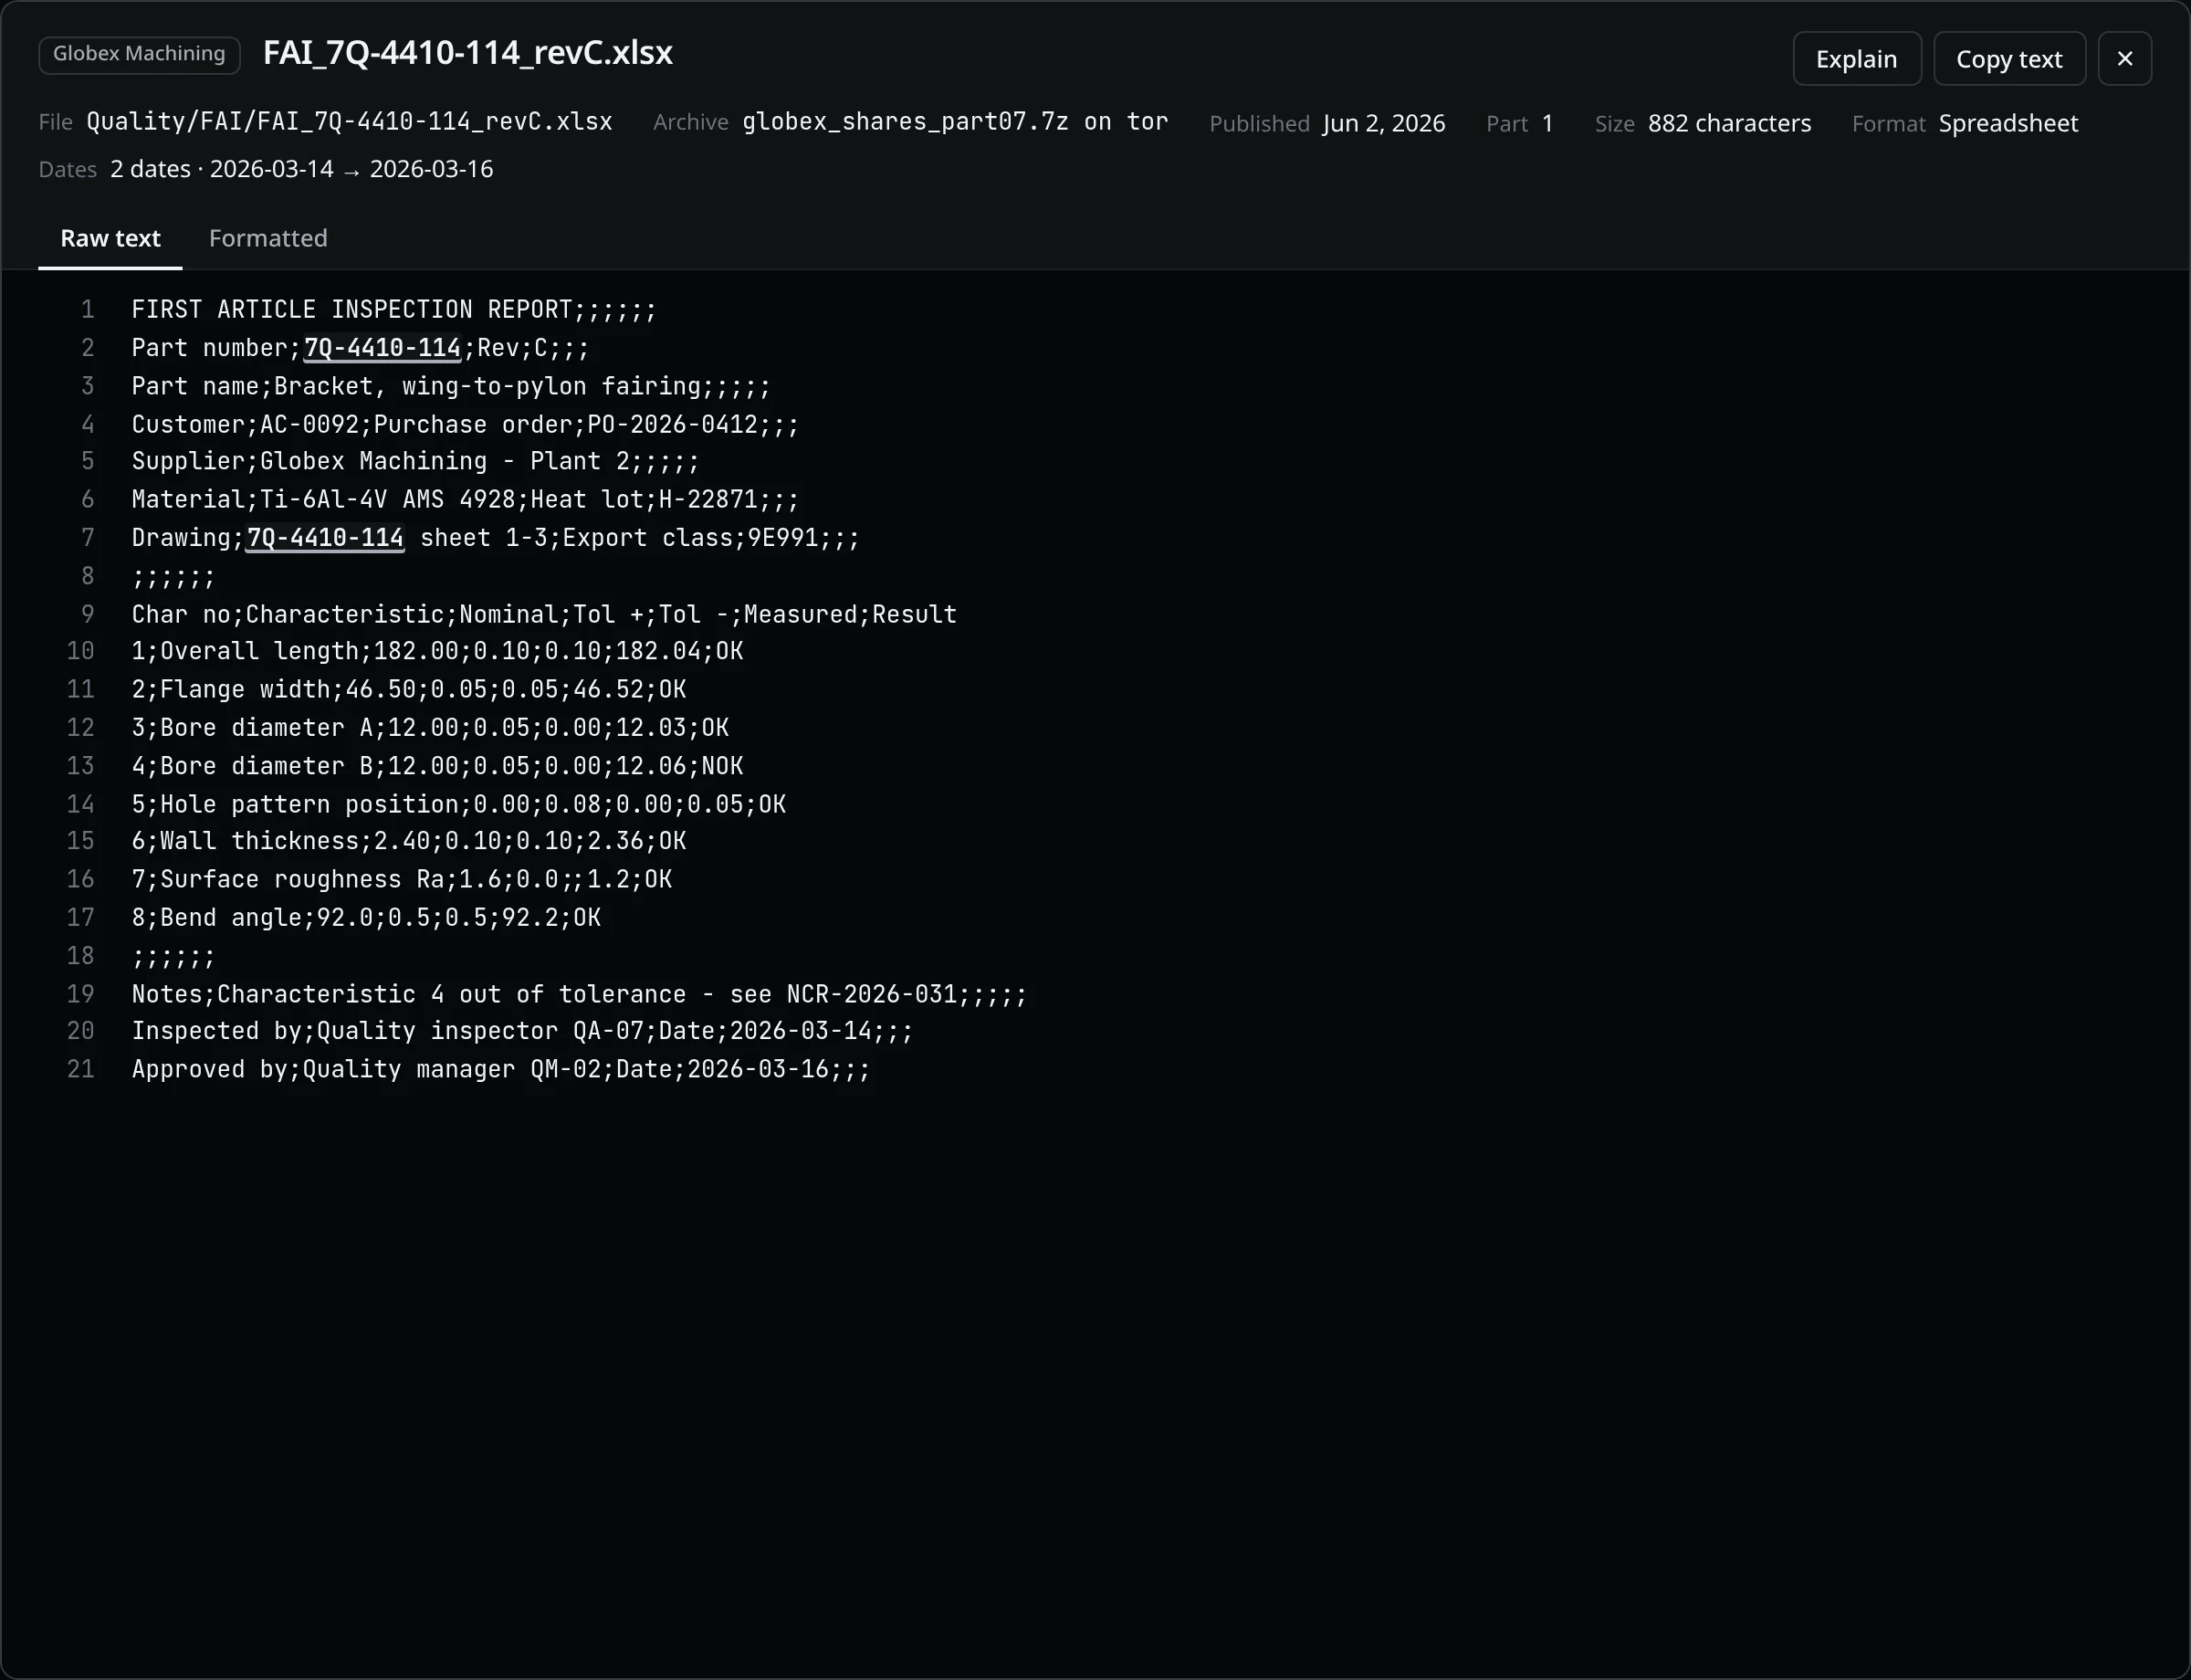
Investigation, document viewer · demo dataDrag to compare
Three offers. Each starts with your free statement.
Search every published leak yourself. Alerts on your keywords. Nothing logged.
From
3 000 €
excl. VAT a year, per organisation
We read every new leak for your scope. One page per finding. Read with you every month.
Plus the whole search engine, included.
From
7 200 €
excl. VAT a year · your organisation and up to three monitored companies
Guarantee
If we miss a significant leak about you, next year is free.
Everything in Monitoring, at the scale of your ecosystem: all your suppliers, a programme, a cluster or a portfolio. Tiers by number of monitored companies.
Plus the whole search engine, included.
Higher tiers
On quote
From four monitored companies upward
Guarantee
If we miss a significant leak about you, next year is free.
No access to your systems. We read only what is already exposed. Results go to you alone.
Why free: it shows you what we do, on your own scope. By hand, it is three weeks of work for two people.
What happens next
Your company, your suppliers, a programme, or the entities you watch. You choose.
What you receive
Guarantee
If we miss a significant leak about you, next year is free.
P.S. Ask before a client or an auditor does.
Developed in France. Our clients include government services, banks, aerospace groups and ERP software vendors. Member of GICAT. Cited by the French Senate. Published at IEEE ICTAI and IFIP SEC.